Author: Tom Hagy
-
Oracle Health Sciences on Pharmacovigilance and Artificial Intelligence
“The potential to use artificial intelligence methods increasingly for the analysis of the increasing amounts of pharmacovigilance data is well understood and many companies are moving (or planning to move) there, and we can predict that routine tasks in pharmacovigilance will in the future be increasingly automated. It will be crucial, however, for regulatory authorities to very clearly provide a position about the use of AI as well as the acceptable level of quality from AI applications. But in parallel with the shaping of those definitions, given the massive increase in their AE case workloads that most companies are currently experiencing, the industry will out of necessity proceed swiftly with the adoption of AI and cloud technologies to reduce their costs and increase their efficiencies.
“Like other industries, the pharmaceutical business and in particular the pharmacovigilance field will see a massive change in their processes in the near future, away from tedious, repetitive manual tasks towards a better utilization of scarce resources, in particular medical and scientific knowledge, for value-adding tasks. It is imperative for all stakeholders – industry, service providers and regulators – to provide an environment in which such a transformation can take place without ever compromising public health or the safety of the individual patient, and ideally providing additional benefit for patients.”
A quote from
Addressing the Data Challenges of PharmacovigilanceDownload the paper from Oracle Health Sciences
We are covering this subject at:
Drug & Device Defense Forum | Oct. 15, 2018 | New York
-
Artificial Intelligence in the Drug and Device Industries
Are Data Divers and Miners Going to Lead Innovation?
The big tech companies are into it. Apple, IBM and Google. Roche is into it. Medtronic, as well. Artificial intelligence has been a big part of innovation in the healthcare space for several years, and its impact is only going to get bigger.
“Artificial intelligence-based healthcare technologies have contributed to improved drug discoveries, tumor identification, diagnosis, risk assessments, electronic health records (EHR), and mental health tools, among others,” writes Blank Rome attorney Brian Higgins in his Artificial Intelligence and the Law Blog (it’s excellent, by the way). [1]
Daniel Faggella of TechEmergence.com writes that machine learning healthcare applications are getting a lot of attention in the press and from the investment community. He adds to the list of machine learning’s impact things like treatment queries and suggestions, and even robotic surgery.
But optimism for AI’s application to drug discovery seems greater than that inspired by other healthcare sectors. One reason for that, Faggella writes, is that compared to other segments where various laws and stakeholder incentives may not align, “drug discovery stands out as a relatively straightforward economic value for machine learning healthcare application creators.” He adds that this application also involves “one relatively clear customer who happens to generally have deep pockets: drug companies.” [2]
Also writing for TechEmergence.com, Kumba Sennaa says doctors may feel threatened at the idea of competing with artificial intelligence tools. Not so in the case of drug makers. “Unlike doctors, pharma companies have every reason in the world to adopt the most cutting-edge technologies in the expensive and lengthy process of drug discovery,” Sennaa writes. “Unlike other applications within healthcare facilities, drug discovery seems to have a clearer path to adoption.” [3]
AI-fueled innovation is, in turn, fueled by data. Lots and lots of data. “And there is no better place to find big data sets than in the healthcare sector,” Higgins says. “According to an article last year in the New England Journal of Medicine, by 2012 as much as 30% of the world’s stored data was being generated in the healthcare industry.”
“Thanks in large part to AI and the availability of health-related data,” Higgins says, “health tech is one of the fastest growing segments of healthcare and one of the reasons why the sector ranks highest on many lists.”
“To be successful,” Higgins predicts, “tomorrow’s healthcare leaders may be those who have access to data that drives innovation in the health tech segment. This may explain why, according to a recent survey, healthcare CIOs whose companies plan spending increases in 2018 indicated that their investments will likely be directed first toward AI and related technologies.”
Related
Given the investment and tremendous opportunity AI provides for the drug and device industries, the chairs of our Fifth Annual Drug & Device Forum are developing a session on the subject. Join us for this and discussion of other important topics on Oct. 15, 2018 in New York.
If you have ideas please reach out to one of our chairs directly or via Ideas@LitigationConferences.com. They are Megan Grossman of Segal McCambridge Singer & Mahoney, Michelle Hart Yeary of Dechert, and Jim Frederick of Goodell DeVries Leech & Dann. Learn more.
Also, on Sept. 27 we are co-producing a webinar titled A.I. Best Practices: Rules and Policies for Using Artificial Intelligence in Your Business. The webinar features John Weaver of the McClane Middleton law firm and contributing author to the Journal of Robotics, Artificial Intelligence & Law. We are producing this in collaboration with growing legal research company Fastcase. Learn more.
Links to the articles cited in this post:
#1. http://aitechnologylaw.com/2018/03/data-driven-health-tech-innovation/
#2. https://www.techemergence.com/machine-learning-healthcare-applications/
#3. https://www.techemergence.com/ai-in-pharma-and-biomedicine/
-
Courtney Klein on Social Media & Security
A Restructured Paradigm for Corporate Teamwork
By Courtney Klein of Soteria Risk Consultants
Social media has become an integral part of everyday life. It’s how some of us get our news, research our opinions, learn about local events, and connect with friends. For the modern western business, it is also immensely important for staying in touch with customers, advertising, and overall visibility. For this reason, many companies employ veritable armies of “Social Media Specialists” that do everything from designing graphics to writing tweets to replying to customer questions and complaints. Some companies interact with each other (such as the hilarious and long-standing Twitter Battle between Wendy’s and McDonald’s), and some use it as their primary form of communication.
Customers, too, know that social media is a way to get in touch with a company – for good reasons and for bad – and while many companies are aware that they will and do receive threats on social media, very few of them have any kind of protocol in place for how to deal with them – and even fewer still encourage their social media teams to pass this information on to or (better yet) work together with their security team. This sort of blasé attitude to threats – either because “it’s not my job” or “they can’t be serious” – leads to real-world ramifications. Incidents such as the April 4th Youtube Shootings (which, we acknowledge, was a failure of many different departments, companies, and law enforcement operations) are a reminder of just how social media “banter” can turn into a real-world nightmare.
Now, in defense of essentially any company guilty of this, Social Media is a new beast that even the best are still trying to get their arms wrapped around. Not only is social media relatively new to the game, but it’s dynamic and ever-changing. What was relevant yesterday no longer will be tomorrow. Updates add new features and kill our favorites, terms of service changes impact business, trends are fleeting but ever so important for a business to understand, customer service issues must be dealt with in a timely fashion. Take all of this and add security concerns on top of the social media specialist’s plate and you’re only going to run into failure. That’s why we at Soteria are such strong believers in having social media and security teams work together every step of the way.
Folding security into the fray … will make a world of difference
With few exceptions, social media teams plan their calendar very carefully. Words must be scripted, graphics must be designed, legal must be consulted; it’s not often that there’s a “last minute tweet that just has to go out right here right now.” With everything else that goes into these seemingly benign releases, folding security into the fray is, ultimately, a minor change, but one that will make a world of difference. Giving the security team insight into what will be posted provides a number of benefits.
The security team will be able to assess what posts may aggravate any known or active threats. In general, security teams like to keep information about who wants to do harm to a company under relative secrecy so as to not unnecessarily alarm staff. As a dedicated intelligence analyst (working for a company with an incredible need to integrate a security function into social media) I personally witnessed a number of occasions where I’d read a post – a perfectly fine, professional post that a normal person wouldn’t bat an eye at – and thought “Oh heck, John Doe isn’t going to be happy about this one,” and upon further investigation discovered that, as suspected, Doe was all sorts of worked up over 260 characters and was heading down to the local office to cause a ruckus. With a little bit of notice, my team could have prepared our local staff for the event and given them adequate time to get ready rather than going into overdrive mode.
 It can help reduce the stress that the social media team feels during the normal course of their duties. Most people know that it’s possible to directly message a company’s customer service group via social media, but often times it’s actually the social media team that is in charge of screening and fielding these messages. On the occasion when a hateful comment or threat comes through, the social media specialist on the receiving end – who likely and rightly doesn’t have a lot of experience with such things – may react in any number of ways, from panic to disbelief. Whatever the response is, the likelihood that they’ll consider sending it to security for analysis without some previous instruction to do so is slim to none. At the very least, giving these staff this simple instruction can mitigate some of the basic issues. At best, it can begin to smooth the path for future growth into a more robust Social Media-Security partnership.
Even security teams with dedicated social media analysts are still constrained by the limits of being human. While your company may have a well staffed social media threat team there is only so much a person can handle at any given time. In reality, though, it’s more likely that whoever is watching social media for threats is also juggling a multitude of different security tasks as well. By working or liaising with your organization’s social media team, you’ll have extra eyes on all the time. Many times, when a person is threatening an organization online they are not directing this information to the company’s inbox or direct messaging their team. Sometimes it’s as simple (and clear) as someone saying “I’m going to go shoot up XYZ Company tomorrow” without any connection to official accounts. Most social media groups monitor for any mention of their company’s name as part of a marketing strategy and to ensure only legitimate accounts are using the company branding. Clearly, this threat is not something that they should be dealing with – but it is certainly the job of corporate security. Even a tenuous partnership between the teams could result in threats like this being effectively handled.
Just as your average security specialist wouldn’t know how to effectively announce a major company event on Twitter, neither will your typical social media analyst have the tools and skills necessary to investigate threats and persons.
Security teams, by the nature of our work, are often able to access information that is not available to social media teams. Tools like Nexis and TLO aren’t given to groups without a legitimate use case, but these tools are often necessary in order to identify a threat actor. Depending on the severity of a threat, this information is often incredibly useful when providing information to the police. They are generally so overworked, underfunded, and understaffed, that having so much information handed to them, especially with an honest, well-documented case file that explains the methodology of your investigation, is a relief, and will help jumpstart an investigation.
Social media teams know who is a regular issue. They know that John Doe sends rude comments to the Instagram inbox every time something is posted. They also know that they have a lot more to their job description than just reading mean comments. The regulars are remembered because of their consistency, but there are other threats who may not come up often enough to remember, and these may be the most dangerous. Likewise, if John Doe suddenly stops sending his vitriol, a social media specialist is likely to feel relief, whereas an intelligence analyst or other security professional might feel apprehension. What’s changed? Where did he go? Was he arrested? Did he find a new target? Or is he planning something that’s taking all of his time? For five years Jarrod Ramos threatened the staff at the Capital Gazette through social media, phone calls, emails, and any means he could find. It was normal for them, though the staff never ignored his threats. But in 2016 he went quiet. The small newspaper had neither the staff nor the resources to figure out why, and it would have been impossible for them to guess that in June of 2018 Ramos would be responsible for the vicious murder of five of their colleagues, but that’s exactly what happened. Likewise, in the reverse, should a case of minor, random harassment become more regular it’s possible an overworked social media specialist might be so harried they just wouldn’t notice. Paying attention to and noticing such trends is well within the wheelhouse of Corporate Security, but our ability to do this work is dependent on good, effective, two-way communication with the people on the receiving end (including and beyond social media).
Finally, and very importantly, it is imperative for any security team to work with the people in their organization if for no other reason than to build relationships. Security is, if we’re being frank, a pain for everyone. While, yes, our goal is to keep people alive and well, completing this task also means we have to be an impediment. The same perimeter security measures that keep out a bad actor also slow down the company’s employee during a torrential downpour. The same check-in procedures that ensure only authorized persons and wanted guests get past the lobby also make the new guy late right before a big meeting when he’s left his badge at home. The same systems that only grant entry to someone with a need-to-access also ruins the forgetful employee’s day when she hears the door click shut behind her just as she notices she left her access card on her desk. Security costs money but doesn’t make it. Security gets in the way of art and gardens and aesthetics. Security is necessary, but it’s also difficult for everyone. By working amicably with as many people as possible throughout an organization and making sure they understand that you’re there to help them get their job done, you are building bridges to better relationships. You’re recruiting ambassadors that can help explain to others why piggybacking is such an issue. You’re educating additional bodies who can come to your team when they notice that outside door isn’t locking when it shuts. You’re expanding the pool of people who will quickly let you know when something doesn’t seem right, rather than just telling you after the fact. And, unlike many teams within many organizations, the social media team is often overwhelmingly comprised of young employees who will be more vocal about their support for you and may even come up with interesting, innovative ways to spread the security word that we may not think of.
The long and short of it is that the world is always changing and evolving and in a field as vast and dynamic as security, we will always be met with new challenges. The most effective way to deal with such hurdles, at least on the front end, may very well be referring to the expertise of other professionals. By working with them instead of against them, we’ll be more able to understand the threats posed to our organizations and communities, and better ensure the continued safety of those who depend on us.
Editor’s note: This article was re-published with the generous permission of the author. She is not the poor soul depicted in the photo above, however, who, for my money, is being a bit dramatic. –Tom Hagy
COURTNEY KLEIN, PSP
Courtney got her start in security while pursuing her master’s degree in criminal justice. Since then, she has served in a consulting capacity for educational institutions, major law firms, local and federal law enforcement, religious organizations, internationally celebrated entertainers, a number of non-profit organizations, a preeminent entertainment company, and state task forces grappling with innovative standards designs.Much of Courtney’s experience also rests in serving on dedicated corporate security teams, focused on everything from basic CPTED design and access control to international travel security and internal fraud investigations. Currently, Courtney proudly serves as the Senior Intelligence Analyst for a major international non-profit, where she uses her experience to identify and monitor individuals who pose a physical or intellectual threat to the organization’s employees, clients, assets and mission.
-
Francoise Gilbert on Colorado’s New Privacy Law: Are You Ready?
Effective Sept. 1, 2018, Colorado will require all entities that process or store certain personal information of Colorado residents, regardless of whether the entity is located within or outside of Colorado, to have formal data security and data disposal programs. This is the result of the adoption of Bill 18-1128 “Concerning Strengthening Provisions for Consumer Data Privacy,” signed into law at the end of May 2018, to amend and supplement existing law …. Previously, the definition of “personal identifying information” under the Colorado law was limited to a resident’s first name or initial and last name in combination with the individual’s Social Security, driver’s license, or identification card number, or a credit or debit card or bank account number, combined with a password or access code. The new definition includes additional forms of identification, such as student, military, passport, and health insurance identification number, as well as other types of information, such as medical information or biometric data. It also includes username or e-email address in combination with a password or security question answers that would permit access to an online account …. Organizations that collect personal identifying information of Colorado residents and that do not yet have the written programs necessary to formalize their data protection practices urgently need to focus on compliance. — Francoise Gilbert, Greenberg Traurig
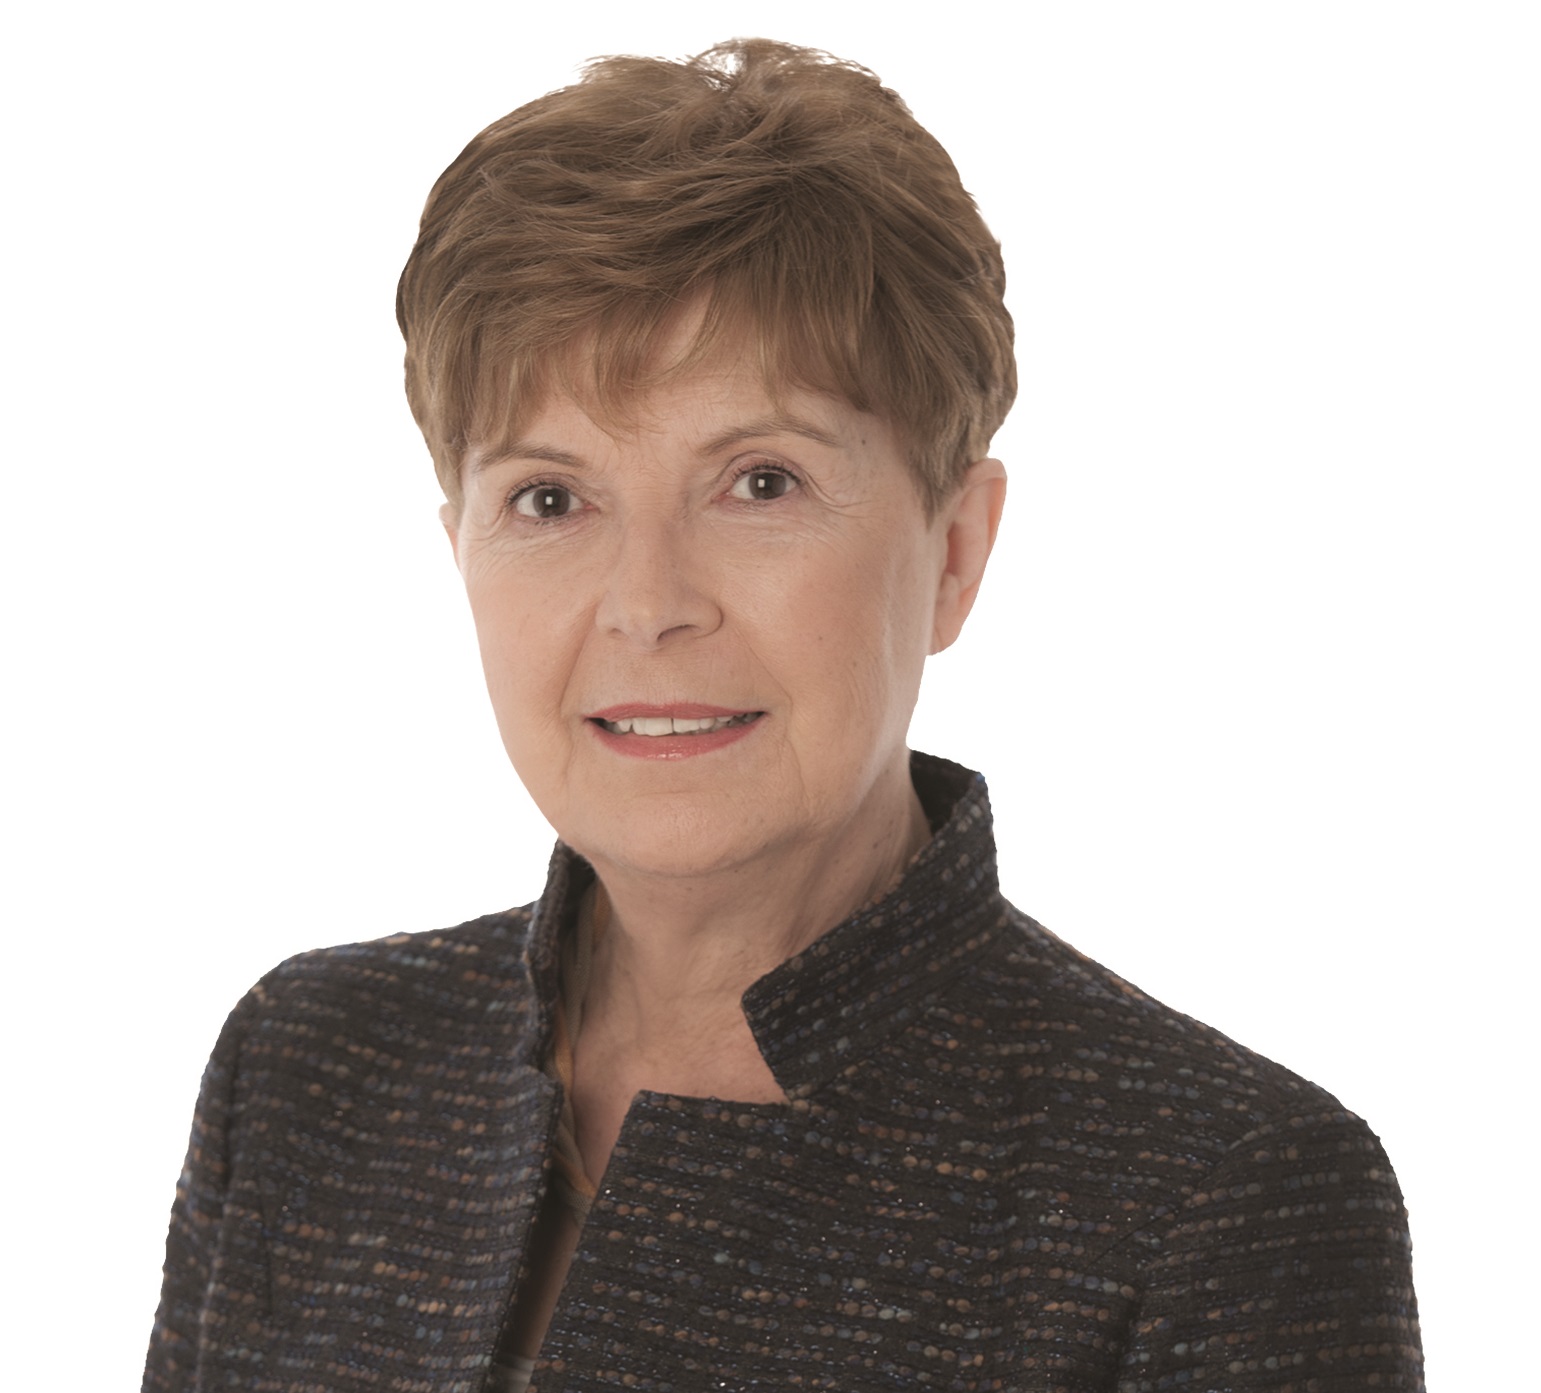 Francoise Gilbert, a partner at Greenberg Traurig, is the author of the two volume treatise “Global Privacy and Security Law” (Wolters Kluwer Publishing), covering 68 countries. Her practice has focused on information privacy and security for more than 25 years. She advises clients on the entire spectrum of domestic and international privacy and cyber security issues legal issues, such as Internet of Things, smart cities, artificial intelligence, analytics, digital advertising and other cutting-edge developments that rely on the extensive use of personal data.
She is one of the featured speakers at the Privacy+Security Forum which takes place Oct. 3-5, 2018, in Washington, DC.
-
A.I. Best Practices: Rules and Policies for Using Artificial Intelligence in Your Business
Explore how cybersecurity breaches impact insurance, risk management, and data privacy with evolving legal and compliance challenges.
[one-third-first]
DATE: Sept. 27, 2018
TIME: 2 p.m. EDT; 1 p.m. CDT; 12 p.m. MDT; 11 a.m. PDT
PLACE: Your computer or mobile device
PRICE: $197* per dial-in site
*Price is good through Aug. 16. After that it’s $247.GROUPS ARE GOOD: Registering qualifies you to multiple attendees at your location.
CLE: 1 credit
Please send CLE questions to
CLE@LitigationConferences.comSPEAKER:
John Frank Weaver
Attorney
McLane Middleton

Your registration includes:
• A site license to attend this webinar (invite as many people in one location as you can fit around your computer at no extra charge).
• Downloadable PowerPoint presentations from our speakers.
• The opportunity to connect directly with speakers during the audience Q&A session.
• At least one-hour of CLE credit.
Produced in collaboration with
and their new
Journal of Robotics, Artificial
Intelligence & Law
[/one-third-first] [two-thirds]
Nearly every industry is adopting or preparing to adopt artificial intelligence applications into their business practices.
That’s exciting. However, there are almost no government regulations for their use and few resources providing best practices that anticipate ethical considerations and forthcoming legal requirements.
This lack of direction poses a serious problem as A.I. applications become more widespread. Businesses are creating their own ad hoc practices without considering the eventual government oversight and ethical consensus, which will result in costs and potential liability later when those companies have to change their practices.
This webinar looks at how your company should approach its A.I. rules and policies in order to minimize the impact of expected government action and cultural norms.
Register now and join our speaker as he explores existing laws addressing privacy and data security, pending A.I. legislation at the state and federal levels, and the recommendations of federal agencies that are most likely to be codified.
The webinar will provide practical guidance for attendees to use when developing internal rules, policies, practices, contracts, and public facing documents. The speaker will rely on relevant existing laws, proposed legislation, and reports from federal agencies that advocate certain public policies for the governance of AI.
What you will learn:
1. The requirements of privacy laws – including GDPR, Canada’s PIPEDA, and the new California privacy statute – that have special application to A.I.
2. Best practices for drafting a public facing privacy policy that addresses your use of A.I.
3. Best practices for preparing internal rules and policies governing your employees’ use of A.I.
4. Best practices for bots and other forms of A.I. that interact with consumers.
5. Best practices for A.I.-specific terms of use and consents.
6. Best practices for addressing A.I. in employee contracts and handbooks.
7. Best practices for addressing A.I. in vendor contracts, including assignment of liability and indemnification obligations.
And more!
Attendees will be able to go back to their companies and review their current A.I. practices, policies, and rules to determine how appropriate they are in light of expected regulations and expectations. The ultimate goal is to avoid costly revisions in response to evolving consumer expectations and government requirements. A little investment now could potentially save a lot of money in revisions changes, PR, and remediation later. — John Weaver, speaker
Speaker
 The webinar speaker, John Frank Weaver, is an attorney with McClane Middleton whose practice focuses on A.I. and autonomous technology. He is the author of Robots Are People Too: How Siri, Google Car, and Artificial Intelligence Will Force Us to Change Our Laws, a contributing writer at Slate focusing on legal issues implicated by AI and autonomous devices, and a columnist for and member of the board of editors of The Journal of Robotics, Artificial Intelligence & Law.
[/two-thirds]
-
McLoughlin on Artificial Intelligence in Banking
“Capital adequacy requirements are not the only kind of regulation that AI is helping banks to meet. An even bigger area is monitoring of trading activities for misconduct and abuse. The Bank of England estimates that misconduct by traders has cost banks a global cumulative of $320 billion to date. For this very large reason, banks are aggressively deploying machine learning to monitor the behavior of their traders and detect unusual behavior.”
Read Michael McLoughlin’s post on LinkedIn.
Michael McLoughlin is Global Digital Transformation Partner & Advocate with Microsoft.
-
Joshua Gold on Cyber Crime and Insurance
With the amount of trickery going into thefts and embezzlements these days, crime insurance companies too often use the many steps involved in a fraudulent scheme to argue that losses are indirect and otherwise uncovered.
The recent decisions of the Second Circuit and Sixth Circuit on the “direct loss” argument and the scope of computer fraud coverage are important victories for policyholders generally, making clear that where the predominant step in the chain is some type of covered fraudulent misconduct involving a computer, a court is not going to entertain a direct loss defense to excuse the insurance company from paying.
As such, policyholders should be familiar with their crime coverage and promptly notify all potentially implicated lines of insurance coverage when a cybercriminal is afoot. — Joshua Gold, Anderson Kill
Read Josh’s complete article.
Joshua Gold is Chair of Anderson Kill’s Cyber Insurance Recovery Practice and was amicus counsel for United Policyholders in the Medidata Solutions, Inc. v. Federal Insurance Company case before the Second Circuit.
-
Halligan, Weyland on Cybersecurity, Trade Secret Asset Management and the Defend Trade Secret Act of 2016
“Cybersecurity protection against outsider theft has largely succeeded, if competently crafted business methods are strictly followed. The more intractable problem of insider theft is now the major concern, and traditional cybersecurity methods are unavailing. The ever-higher digital barriers placed around the corporation and its sensitive data are no defense against data theft by people allowed inside the digital walls in the normal course of business.”
Read their complete post on LinkedIn.
R. Mark Halligan is a Partner and Trial Lawyer at FisherBroyles, LLP. Mr. Halligan has taught Advanced Trade Secrets Law in the John Marshall Law School LLM program for 24 years.
Richard F. Weyand is the President of the Trade Secret Office, Inc. www.thetso.com
See R. Mark Halligan and Richard F. Weyand Trade Secret Asset Management 2018: A Guide to Information and Asset Management Including RICO and Blockchainavailable on Amazon. https://www.amazon.com/dp/0997070986
-
Willis Towers Watson: Cyber Risk Top D&O Concern
Based on their survey, Willis Towers Watson says cyber risk continues to top the list of concerns for directors and officers (right up there with employee claims). As for coverage, while they care about price, things like their relationship with the carriers and how well they handle claims are critical elements.
And, maybe one key reason cyber events keep happening: “Only 13% of board members feel that their organizations learn from past cyber mistakes.”
Read the results of the Willis Towers Watson survey.