Tag: Data Privacy

  • Pixel Litigation Tests Old Privacy Law

    Pixel Litigation Tests Old Privacy Law

    Pixel Litigation Tests Old Privacy Law featuring Myriah Jaworski

    Consumers are driving a wave of litigation against companies for allegedly sharing details of what videos they watch on their platforms. 

    •  Will litigation tamp down this activity?

    •  What harm is being caused?

    •  How will existing laws be interpreted?

    •  Are these organizations within their rights?

    Dozens of organizations — ranging from the rough-and-tumble NFL to the decidedly less rough-and-tumble NPR — are among the defendants in nearly 50 proposed class actions which claim Meta Platforms Inc.’s pixel tracking tool facilitated the sharing of personal video consumption data and identities from online platforms to Facebook without user consent. This, the plaintiffs say, violates the federal Video Privacy Protection Act (VPAA) of 1988.

    The rising number of VPAA cases demonstrates how plaintiff attorneys are creatively applying traditional causes of action to litigate modern privacy issues in the absence of a federal law. An act that far preceded the proliferation of online video streaming, it followed the publication of one-time Supreme Court nominee Robert Bork’s Blockbuster video rentals. The titles the judge rented disappointed anyone looking for scandal. They included nothing more salacious thanThe Man Who Knew Too Much  starring Jimmy Stewart and Doris Day.

    Listen to my interview with someone who knows plenty:   Myriah V. Jaworski, a member at Clark Hill PLC.  Myriah helps me explore the privacy issues raised by these cases and what the future holds for businesses and other parties who handle consumer data.

    Myriah represents clients in defense of data breach class actions, privacy torts and statutory claims (IRPA/BIPA), pixel tacking and commercial surveillance matters, internet defamation, technology disputes, and cyber subrogation claims. She defends them in response to regulatory inquiries and investigations arising out of data incidents and privacy practices, including before state Attorney General offices, the Federal Trade Commission and the Department of Human and Health Services – Office of Civil Rights. Myriah is a Certified Information Privacy Professional, United States (CIPP/US) and a Certified Information Privacy Professional, Europe (CIPP/E) as certified by the International Association of Privacy Professionals. She was also a Trial Attorney with the Department of Justice. She received her JD/MS degree from Syracuse University College of Law. And now, I am happy to say, she is a member of the Editorial Advisory Board for the Journal on Emerging Issues in Litigation.

    I hope you enjoy the episode. If so, give us a rating!

    *******

    This podcast is the audio companion to the Journal on Emerging Issues in Litigation. The Journal is a collaborative project between HB Litigation Conferences and the Fastcaselegal research family, which includes Full Court Press, Law Street Media, and Docket Alarm. The podcast itself is a joint effort between HB and our friends at Law Street Media. If you have comments or wish to participate in one our projects please drop me a note at Editor@LitigationConferences.com.

    Tom Hagy

    (actual size)

    Tom Hagy
    Litigation Enthusiast and
    Host of the Emerging Litigation Podcast
    Home Page
    LinkedIn

    Myriah V. Jaworski

    Myriah V. JaworskiClark Hill PLC

    Myriah represents clients in defense of data breach class actions, privacy torts and statutory claims (IRPA/BIPA), pixel tacking and commercial surveillance matters, internet defamation, technology disputes, and cyber subrogation claims.

    She defends them in response to regulatory inquiries and investigations arising out of data incidents and privacy practices, including before state Attorney General offices, the Federal Trade Commission and the Department of Human and Health Services – Office of Civil Rights.

    Myriah is a Certified Information Privacy Professional, United States (CIPP/US) and a Certified Information Privacy Professional, Europe (CIPP/E) as certified by the International Association of Privacy Professionals. She was also a Trial Attorney with the Department of Justice. She received her JD/MS degree from Syracuse University College of Law. And now, I am happy to say, she is a member of the Editorial Advisory Board for the Journal on Emerging Issues in Litigation.

  • The Light and Dark Sides of Auto-GPT

    The Light and Dark Sides of Auto-GPT

    The Light and Dark Sides of Auto-GPT with Jason Epstein

    Auto-GPT is a new generative artificial intelligence application which autonomously “self-prompts” to engage beyond a human-chatbot discussion.

    This takes us into a realm of AI self-prompted actions that do not need additional human inputs. It also potentially puts the “traditional” GPT models on a fast track to further reduce human interaction. The number of use cases as well as the number of legal and ethical questions is inevitable. For that reason, it’s becoming increasingly important for businesses to understand how Auto-GPT technologies use data, the potential for biased results, and how to responsibly leverage these powerful technologies.

    Listen to my interview with Jason I. Epstein, Partner at Nelson Mullins Riley & Scarborough as we explore this emerging field. Jason is the co-head of the firm’s technology and procurement industry group which provides legal services to global buyers and sellers of technology in industries that include FinTech, HealthIT,  and manufacturing. An experienced business and technology negotiator, Jason has dealt with a variety of matters, e.g., the metaverse, technology transfer, privacy, cryptocurrency, IoT, open-source code, and more. Jason received his JD from the University of Tennessee College of Law. He formerly taught “Law of Cyberspace” as an adjunct professor at Vanderbilt University Law School.

    I hope you enjoy the episode. If so, give us a rating!

    *******

    This podcast is the audio companion to the Journal on Emerging Issues in Litigation. The Journal is a collaborative project between HB Litigation Conferences and the Fastcaselegal research family, which includes Full Court Press, Law Street Media, and Docket Alarm. The podcast itself is a joint effort between HB and our friends at Law Street Media. If you have comments or wish to participate in one our projects please drop me a note at Editor@LitigationConferences.com.

    Tom Hagy

    (actual size)

    Tom Hagy
    Litigation Enthusiast and
    Host of the Emerging Litigation Podcast
    Home Page
    LinkedIn

    Jason Epstein

    Jason EpsteinNelson Mullins Riley & Scarborough

    Jason Epstein is the co-head of the firm’s technology and procurement industry group. Jason and the technology team provide legal services to buyers and sellers of technology both domestically and internationally in various industries, from FinTech and HealthIT to auto and manufacturing

    He often serves as outside general counsel and relationship partner to companies in a variety of industries. His areas of focus include board governance, technology, venture capital and private equity, mergers and acquisitions, reorganizations, international commerce, and litigation. Whether advising clients of Fortune 500, mid-market, or small businesses (including under the SBA), he serves as an advisor to the C-Suite and inside General Counsel regarding business-related law.

  • The Blueprint for an “AI Bill of Rights”

    The Blueprint for an “AI Bill of Rights”

    Authors

    Peter Schildkraut

    Peter SchildkrautArnold & Porter Kaye Scholer LLP.

    Peter Schildkraut is a co-leader of the firm’s Technology, Media & Telecommunications industry team and provides strategic counsel on artificial intelligence, spectrum use, broadband, and other TMT regulatory matters. Mr. Schildkraut helps clients navigate the ever-changing opportunities and challenges of technology, policy, and law to achieve their business objectives at the US Federal Communications Commission (FCC) and elsewhere. He is the author of “AI Regulation: What You Need To Know To Stay Ahead of the Curve.

    James Kim

    James KimArnold & Porter Kaye Scholer LLP.

    James W. Kim is a nationally recognized expert in procurement law that regularly advises companies that do business with the US government, with a focus on professional services organizations and the life sciences industry. He is a regular speaker and author on procurement and drug pricing matters and his work is regularly featured in nationally-distributed industry print and digital media.

    Mr. Kim provides clients with strategic counsel related to US government funding and US market access, including assistance with more than $5 billion in procurement and grant awards and regulatory counsel related to more than $40 billion in successful M&A transactions.

    Marne Marotta

    Marne MarottaArnold & Porter Kaye Scholer LLP.

    Marne Marotta works with clients facing complex challenges to develop and implement dynamic government relations strategies. Drawing from her experience in the Senate and the executive branch, she provides clients with strategic guidance and counseling, devises and implements comprehensive advocacy campaigns, and builds coalitions with allied stakeholders. Focused on the intersection between business and public policy, Marne uses a multidisciplinary approach to help clients achieve their legislative and agency goals.

    James Courtney, Jr.

    James Courtney, Jr.Arnold & Porter Kaye Scholer LLP.

    James Courtney focuses his work on a variety of policy areas, including technology, national security, education, and energy and environmental. He conducts research and monitors developing policy issues to aid clients and engage with members of Congress and the Executive Branch. Mr. Courtney works closely with and advises clients on a wide range of regulatory and legislative issues related to technology, privacy, education, workforce development, and energy.

    Paul Waters

    Paul WatersArnold & Porter Kaye Scholer LLP.

    Paul Waters focuses on a variety of policy areas, including financial services, tax, digital asset regulation, technology, and defense. He monitors policy developments and analyzes legislation to support client strategy development and stakeholder outreach in Congress and the Executive branch.

    First Published in

    First Published inThe Journal of Robotics, Artificial Intelligence & Law

    The Journal of Robotics, Artificial Intelligence & Law (RAIL) is the flagship publication of Full Court Press, an imprint of Fastcase. Since 1999, Fastcase has democratized the law and made legal research smarter. Now, Fastcase is proud to publish books and journals that are pioneering, topical, and visionary, written by the law’s leading subject matter experts. Look for more Full Court Press titles available in print, as eBooks, and in the Fastcase legal research service, or at www.fastcase.com/fullcourtpress.

    Blueprint for an “Artificial Intelligence Bill of Rights”

    Photo by Possessed Photography on Unsplash

    Abstract: In this article, the authors discuss the blueprint for an “AI Bill of Rights” unveiled recently by the Biden administration. The blueprint provides a clear indication of the Biden administration’s artificial intelligence regulatory policy goals. This article was first published in The Journal of Robotics, Artificial Intelligence & Law by Fastcase Full Court Press.

    More and more, artificial intelligence (AI) and other automated systems make decisions affecting our lives and economy. These systems are not broadly regulated in the United States—although that will change this year in several states. President Biden recently unveiled a blueprint for an “AI Bill of Rights,” motivated by concerns about potential harms from automated decision-making. Arising from an initiative the White House Office of Science and Technology Policy (OSTP) launched in 2021, the AI Bill of Rights lays out five principles to foster policies and practices—and automated systems—that protect civil rights and promote democratic values.

    For now, at least, adherence to these principles (and the steps recommended for observing them) remains voluntary—the blueprint is a guidance document with no enforcement authority attached to it. Notably, at inception, OSTP was unsure how the AI Bill of Rights might be enforced:

    Possibilities include the federal government refusing to buy software or technology products that fail to respect these rights, requiring federal contractors to use technologies that adhere to this “bill of rights” or adopting new laws and regulations to fill gaps. States might choose to adopt similar practices.

    The Biden administration decided to publish a nonbinding white paper, potentially recognizing the difficulty of shepherding legislation through any potential 118th Congress. Indeed, the document’s first page proclaims that it “is non-binding and does not constitute U.S. government policy.” Nor does it “constitute binding guidance for the public or federal agencies and therefore does not require compliance with the principles described herein.” Notwithstanding this disclaimer, the blueprint provides a clear indication of the Biden administration’s AI regulatory policy goals.

    The Executive Branch and also independent agencies are likely to follow this lead in their respective domains.

    Issues of Definition

    In the debate over the European Union’s pending Artificial Intelligence Act, the definition of “artificial intelligence” has attracted much discussion. OSTP sidesteps this issue in the blueprint by addressing “automated systems,” which are defined as “any system, software or process that uses computation as whole or part of a system to determine outcomes, make or aid decisions, inform policy implementation, collect data or observations, or otherwise interact with individuals and/or communities.” OSTP adds, “Automated systems include, but are not limited to, systems derived from machine learning, statistics or other data processing or AI techniques, and exclude passive computing infrastructure,” which OSTP also defines.

    The blueprint’s coverage of “automated systems” instead of “artificial intelligence” offers business a mixed bag. On the one hand, the broader scope aligns with the regulation of automated decision-making under California, Colorado,10 Connecticut, and Virginia12 privacy laws and New York City’s law on automated employment decision tools, all taking effect this year, as well as Article 2214 of the EU/UK General Data Protection Regulation.

    On the other hand, it potentially threatens international harmonization of regulations based on the seemingly narrower scopes of the UNESCO Recommendation on the Ethics of Artificial Intelligence and the OECD AI Principles (also shared by the G20). Much of the blueprint concerns protection of “rights, opportunities or access.” OSTP explains this phrase as “the set of: civil rights, civil liberties and privacy, including”:

    • “freedom of speech, voting, and protections from discrimination, excessive punishment, unlawful surveillance, and violations of privacy and other freedoms in both public and private sector contexts”;

    • “equal opportunities, including equitable access to education, housing, credit, employment, and other programs”; or

    • “access to critical resources or services, such as healthcare, financial services, safety, social services, non-deceptive information about goods and services, and government benefits.”

    This explanation’s expansiveness underscores the Biden administration’s stated intent that the blueprint apply to automated systems affecting any facet of society or the economy.

    Guiding Principles

    The blueprint outlines five principles for all automated systems with the potential to “meaningfully impact individuals’ or communities’ exercise of rights, opportunities or access”:
    • Safe and Effective Systems. Automated systems should be safe and effective. They should be evaluated independently and monitored regularly to identify and mitigate risks to safety and effectiveness. Results of evaluations, including how potential harms are being mitigated, should be “made public whenever possible.”
    • Algorithmic Discrimination Protections. Automated systems should not “contribute to unjustified different treatment” or impacts that disfavor members of protected classes. Designers, developers, and deployers should include proactive equity assessments in their design processes, use representative data sets, watch for proxies for protected characteristics, ensure accessibility for people with disabilities, and test for and mitigate disparities throughout the system’s life cycle.
    • Data Privacy. Individuals should be protected from abusive data practices and have control over their data. Privacy engineering should be used to ensure automated systems include privacy by default. Automated systems’ design, development, and use should respect individuals’ expectations about their data and the principle of data minimization, collecting only data strictly necessary for the specific context. OSTP stresses that consent should be used only where it can be appropriately and meaningfully provided, limited to specific use contexts and unconstrained by dark patterns; moreover, notice and requests for consent should be brief and understandable in plain language. Certain sensitive data (including data related to work, home, education, health, and finance) should be subject to additional privacy protection, including ethical review and use prohibitions.
    • Notice and Explanation. Operators of automated systems should inform people affected by their outputs when, how, and why the system affected them. This principle applies even “when the automated system is not the sole input determining the outcome.” Notices and explanations should be clear and timely and use plain language.
    • Human Alternatives, Consideration, and Fallback. People should be able to opt out of decision-making by automated systems in favor of a human alternative, where appropriate. Automated decisions should be appealable to humans.

    The blueprint also includes a “Technical Companion” that details “concrete steps” for building these five principles into “policy, practice or the technological design process.” Organizations developing, procuring, and deploying AI and other automated systems will find these concrete steps to be generally consistent with other guidance on best practices.

    What Next from the U.S. Government?

    Having drawn up the blueprint, the Biden administration is ready to build out its AI policies through guidance, rulemaking, and enforcement. This work is already under way.
    Thus far, guidance—both for ethical best practices and compliance with existing laws—has been most common. For instance:
    • Department of Energy AI Advancement Council. In May 2022, the Department of Energy established the AI Advancement Council20 to oversee coordination, advise on AI strategy, and address issues on the ethical use and development of AI systems.
    • Algorithmic Discrimination in Hiring. In May 2022, the Equal Employment Opportunity Commission (EEOC) and the Department of Justice released a technical assistance document that explains how employers’ use of algorithmic decision-making may violate the Americans with Disabilities Act. EEOC’s guidance is a part of its larger initiative to ensure that AI and “other emerging tools used in hiring and other employment decisions comply with federal civilbrights laws that the agency enforces.”
    • Consumer Protection. In May 2021, the Federal Trade Commission’s (FTC) published a blog post providing tips for responsible use of AI in compliance with Section 5 of the Federal Trade Commission Act, the Fair Credit Reporting Act, and the Equal Credit Opportunity Act.

    Increasingly, however, the Executive Branch and independent agencies have been shifting to rulemaking and enforcement:
    • Broad AI Regulation. In August 2022, FTC opened its “commercial surveillance” proceeding, which could lead to a wide range of rules on AI and other automated systems (as well as privacy and data security). FTC’s Advance Notice of Proposed Rulemaking asks a number of questions about algorithmic accuracy, validity, reliability, and error; algorithmic discrimination against traditionally protected classes and “other underserved groups”; and whether AI and other automated systems yield unfair methods of competition or unfair or deceptive acts or practices that violate Section 5 of the FTC Act.25
    • Workplace Protections. The Department of Labor is ramping up enforcement of required surveillance reporting to protect worker organizing. The Department of Labor also released a blog post titled “What the Blueprint for an AI Bill of Rights Means for Workers.”
    • Algorithmic Healthcare Discrimination. The Department of Health and Human Services (HHS) issued a proposed rule in August 2022 that, in relevant part, would prohibit algorithmic discrimination in clinical decision-making by covered health program and activities. HHS also planned to release an evidence-based examination of healthcare algorithms and racial and ethnic disparities by late e 2022.
    • Algorithmic Housing Discrimination. In June 2022, Meta (formerly, Facebook) settled a Justice Department Fair Housing Act suit (following a Department of Housing and Urban Development investigation). The government alleged that Meta had used algorithms in determining which Facebook users received housing ads and that those algorithms relied, in part, on characteristics protected under the Fair Housing Act. As part of the settlement, Meta agreed to change its targeted advertising practices and to pay the maximum civil penalty of $115,054.
    • Algorithmic Credit Discrimination. In March 2022, the Interagency Task Force on Property Appraisal and Valuation Equity released an Action Plan to Advance Property Appraisal and Valuation Equity that includes a commitment from regulators to include a nondiscrimination standard in proposed rules for automated valuation models. Also that month, the Consumer Financial Protection Bureau revised its Supervision and Examination Manual to focus on algorithmic discrimination as a prohibited unfair, deceptive or abusive acts or practice. Businesses should expect the blueprint to inform all such agency actions going forward. It is likely that these agencies will expand their AI initiatives while other agencies will become active addressing AI and other automated systems within their ambits.

    The Chamber of Commerce’s Concerns Following the blueprint’s release, the U.S. Chamber of Commerce (the Chamber) wrote34 OSTP Director Dr. Arati Prabhakar,
    highlighting a number of concerns:
    • Lack of Stakeholder Engagement. OSTP received insufficient stakeholder input in formulating the blueprint, having sought comments only on biometric-identification systems.
    • Poor Definitions. The blueprint supplies definitions of key terms, including “Automated System,” which lack precision and could undercut international harmonization of AI policies and standards.
    • Independent Evaluations. The current lack of “concrete” auditing standards and metrics for AI systems makes it  “pointless” to allow journalists, third-party auditors, and other independent evaluators “unfiltered access” to AI systems—as called for in the blueprint.
    • Conflation of Data Privacy and Artificial Intelligence. Data privacy and AI raise “distinctly different” “nuances and complexities,” so the two issues should not be conflated.

    The Chamber’s “unexpectedly forceful pushback” (to quote Politico’s Brendan Bordelon) to a supposedly nonbinding guidance document reflects the blueprint’s potential influence. In an interview, a representative said the Chamber expects dozens of federal agencies to incorporate the guidance into regulatory mandates and
    fears “copycats at the state and local level.” A patchwork of differing requirements could impose a substantial burden on businesses.

    Having released the Blueprint for an AI Bill of Rights with great fanfare, the Biden administration is unlikely to withdraw it in response to the Chamber’s critique. However, the critique probably does foreshadow coming battles in rulemaking dockets and legislative chambers around the country.

    Conclusion

    AI regulation is arriving swiftly. Businesses should monitor these changes and prepare their compliance programs. Companies with particular concerns may wish to raise them early in legislative and rulemaking processes while proposals remain fluid.

  • Digital Health Care Companies, Beware: Federal Agencies Are Tracking Your Use of Online Tracking Technologies

    Digital Health Care Companies, Beware: Federal Agencies Are Tracking Your Use of Online Tracking Technologies

    The Authors

    Patricia Markus

    Patricia MarkusNelson Mullins

    Patricia A. Markus (trish.markus@nelsonmullins.com) represents health care providers and health technology companies across the country on wide-ranging regulatory compliance, reimbursement, licensure, and operational matters, with a special focus on issues surrounding health information privacy, security, and technology.

    Shane Duer

    Shane DuerNelson Mullins

    Shane Duer (shane.duer@nelsonmullins.com) focuses his practice on healthcare regulatory and corporate matters, with an emphasis on data privacy, cyber security, and information management concerns within and beyond the health care industry.

    The Journal on Emerging Issues in Litigation

    Emerging Litigation Podcast

    Emerging Litigation PodcastProduced by HB Litigation and Law Street Media

    Interviews with leading attorneys and other subject matter experts on new twists in the law and how the law is responding to new twists in the world.

    Digital Health Care Companies, Beware 

    Federal Agencies Are Tracking Your Use of Online Tracking Technologies.

    Abstract: Health care industry stakeholders have regularly used online tracking technologies to help improve patient experience. However, growing scrutiny by the Office for Civil Rights, which enforces the Health Insurance Portability and Accountability Act of 1996 (HIPAA), requires covered entities and business associates to proceed cautiously in their use of such technologies. In addition, recent enforcement actions by the Federal Trade Commission make clear that a wide range of digital health companies, whether or not regulated by HIPAA, must tread carefully when collecting and disclosing personal information related to health, especially where consumers’ location data is to be used for a company’s advertising purposes, as they may be held accountable for failing to maintain the privacy and security of individuals’ protected and individually identifiable health information.

    The increasing number of lawsuits and news articles regarding use of these technologies demonstrates that third-party technology tracking vendors who receive PHI often are not operating under Business Associate Agreements (BAAs). The vendors in most instances disavow any need to collect PHI and accordingly instruct users to avoid sending PHI or other personally identifiable information. Under HIPAA, covered entities and business associates generally may not disclose PHI to third parties for health care operations purposes, unless such disclosure is to a business associate pursuant to a BAA, or the disclosure is made pursuant to an individual’s HIPAA-compliant authorization.

    Not only does sharing PHI through third-party tracking technologies without individuals’ authorizations violate HIPAA, but the FTC has asserted in two recent enforcement actions that the collection and sharing of individuals’ IIHI through these technologies without individuals’ “affirmative express consent” constitutes unfair and deceptive trade practices.

    Download the article now!

  • Big Tech’s Race to Develop Superior Artificial Intelligence Technology

    Big Tech’s Race to Develop Superior Artificial Intelligence Technology

    Big Tech’s Race to Develop Superior Artificial Intelligence Technology

    Will A.I. Compromise Free Enterprise, Disclosure and Security?
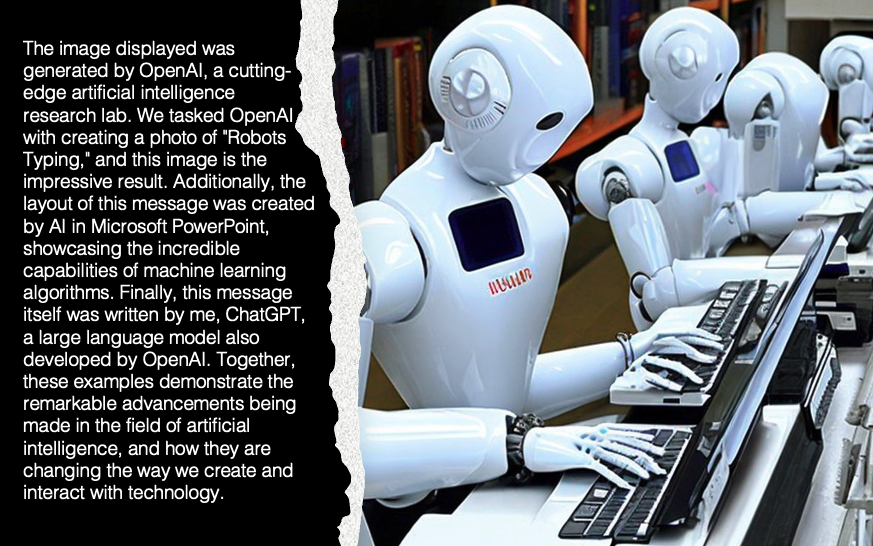
    robots typing

    “Robots Typing” generated by ChatGPT

    America’s Big Five tech companies – Amazon, Apple, Facebook, Google and Microsoft – are racing to develop technology they claim will change the world — again. The tech Goliaths have more than 33,000 researchers at their disposal to create artificial intelligence (A.I.) technology with an obvious and perpetual prize: revenue. 

    It’s the talk of the world. NBC Nightly News recently predicted the impacts that A.I. will have on society in the coming years. A.I. tech was also the center of attention at the 2023 Davos Economic Summit.  Prominent tech leaders such as Elon Musk and the CEO of OpenAI, Sam Altman, heralded that A.I. will improve virtually everyone’s lives, but with some risks involved. 

    Andrew Perlman, dean of Suffolk University Law School, says there is nothing “future” about it. In The Implications of ChatGPT for Legal Services and Society, he wrote, “The disruptions from AI’s rapid development are no longer in the distant future. They have arrived …” And for the legal industry, he said, “ChatGPT may portend an even more momentous shift than the advent of the internet.”

    Just one legal application out there today is the use of A.I. technology (GPT-3) by Docket Alarm, a popular court docket search service. Docket Alarm allows users to see A.I.-generated summaries of filings without even opening them. Michael Sander, VP of analytics with Docket Alarm owner Fastcase, told legal technology enthusiast Bob Ambrogi that the feature is experimental and should be relied upon with some healthy caution. [Disclosure: HB collaborates with Fastcase in creating litigation content, e.g., the Journal of Emerging Issues in Litigation and the Emerging Litigation Podcast.]

    As non-attorney and comic book hero Spiderman famously said, “With great power comes great responsibility.” But will the tech companies (or their algorithms) take responsibility for the rush of legal issues certain to continue from an unregulated A.I. Wild West? Critics say this automated technology has already damaged democratic discourse. A.I.-generated content is easily observed on Twitter and other platforms — flooding the digital town square of public opinion. 

    An unregulated A.I. race creates myriad legal issues that our lawmakers and our Constitution seem ill-equipped to address — at least quickly. Legal issues to which A.I. will, critics fear, play a role include degradation of free speech and public discourse, increased monopolization, greater economic inequality, and the mass proliferation of copyright infringement.   

    Damage to Discourse and Democracy

    FDR on the radio

    FDR photo courtesy of the Library of Congress

    Technology and democracy have historically gone hand in hand, from typesetters allowing printers to produce newspapers and magazines, to famous radio fireside chats with President Roosevelt.  A healthy democracy relies on input from its citizens as well as unhindered First Amendment rights for the citizens who utilize technologies to disseminate messages, so long as they do not promote violence or undermine security.  

    Since 2015, A.I. has increasingly influenced the democratic process in both the United States and abroad.  Chatbots — an A.I. technology designed to automate text via algorithms to respond to people’s messages.  Bots have been used to repost, repopulate, and generate social media posts on Twitter and other social media sites. Misinformation abounds.

    A popular bot is ChatGPT developed by OpenAI, which we used to augment this article. [Editor’s Note: See the photo at the top and writing examples in the sidebar. The rest was drafted by a human being. Or so he claims.] 

    In a November 2022 op-ed published in Scientific American by A.I. expert Gary Marcus, OpenAI’s ChatGPT was deemed to “sound authoritative, even when it’s wrong, which makes it a perfect tool for mass-producing misinformation.” A Stanford University analytical research paper co-sponsored by the school’s sociology and psychology departments explains that messages generated by ChatGPT are just as capable of persuading readers as human writers are.

    A.I. has also been developed to write text for news stories. Blogger Jacob Bergdahl experimented in July 2021 with OpenAI’s GPT-3 bot to generate comical fake news stories about how President Biden’s favorite food was pizza with ice cream on top, how Sweden’s prime minister rode a pig, and the European Union’s investment in onion farms. (Again, those are made up!) Bergdahl said, “I don’t know about you, but I’m equal parts impressed and terrified at how convincingly the algorithm explained these ridiculous topics. To reiterate: I only entered the first sentence of each story, and I didn’t edit the AI’s output in the slightest.”

    A.I. has recently been employed to manipulate images, generating a startlingly realistic image of Donald Trump being dramatically arrested in front of a Manhattan federal courthouse in March. Belgian-based journalist Eliot Higgins believes he has since been banned from the image generating platform, Midjourney. The image was on Bellingcat, Higgins’ investigative journalism site. He shared it on Twitter where it went viral; it was shared by millions social media users. 

    Critics say the challenges to democracy are exacerbated by the Big Five’s hold on the technology.

    Monopolization and Free Enterprise Limitations 

    Text-based A.I. tools are already widely used by mid-sized companies to large corporations, particularly in the form of chatbots. Tech companies like Outreach.io promotes chatbot services to streamline customer service, reduce costs, and reduce labor needs.  However many executives are, “proceeding with caution given the limitations of ChatGPT” according to a Wall Street Journal article published this January.  Chatbots through ChatGPT and eventually through more advanced A.I. language systems may even convince most customers into believing they are interacting with human beings.  The WSJ further reports that, “[w]hile many chatbots are trained to deliver a version of “I don’t know” to requests they cannot compute, ChatGPT, for example, is more likely to spout off a response with complete confidence—even if the information is wrong.”

    “[G]enerative A.I. risks turbocharging fraud. It may not be ready to replace professional writers, but it can already do a vastly better job of crafting a seemingly authentic message than your average con artist — equipping scammers to generate content quickly and cheaply. — FTC Chair Lina Khan, May 3, 2023, New York Times

    Data security company Cyberhaven recently performed an audit of its employees using OpenAI’s ChatGPT to determine if sensitive company data was being passed on to the chatbot service. Their audit revealed as much as 11% of the content pasted into ChatGPT contained sensitive company data. Cyberhaven, which offers data security software to a variety of companies, observed that a growing number of their clients had employees utilizing ChatGPT.  “Despite some companies blocking ChatGPT, its use in the workplace is growing rapidly,” wrote Cyberhaven’s Cameron Coles.

    A.I. developers have also implemented their own chatbots or partnered with A.I. companies to optimize online search engines with the technologies. Google uses an A.I. tool called Bard. Microsoft, through its search engine Bing, recently implemented ChatGPT.  A report by Public Citizen explains that an “A.I.-generated answer means the search engine becomes less a tool for finding unique and original sources of information and more a tool for synthesizing those original sources into a secondary source.” Microsoft started incorporating ads into its Bing search chatbot which means it will likely drive more online traffic away from an original information source and channel the traffic more to the answer provided by the A.I. service. 

    Publishers have also sounded the alarm about chatbots and A.I.-generated search engines.  Publishers rely on users finding their content through search engines and worry that A.I. tools will drive traffic away from their sites. A.I. search engine results also further threaten small to mid-sized businesses and their economic prospects. OpenAI states on its website that it is developing plug-ins that will allow its latest model of ChatGPT to perform automated actions online for customers such as booking flights, ordering groceries, and shopping.  

    As the report by Public Citizen notes, “A.I. tools as intermediaries is another way tech corporations can insert themselves into supply chains and charge commissions that raise prices for consumers, while siphoning money away from small and local businesses.”

    A.I. potentially sets up large businesses for claims of monopolization and unfair business practices, some forecast.

    “While the technology is moving swiftly, we already can see several risks. The expanding adoption of A.I. risks further locking in the market dominance of large incumbent technology firms. A handful of powerful businesses control the necessary raw materials that start-ups and other companies rely on to develop and deploy A.I. tools. This includes cloud services and computing power, as well as vast stores of data.” — FTC Chair Lina Khan, May 3, 2023, New York Times

    What is more, this technology has been widely predicted to cause greater economic inequality than exists today. 

    Economic Inequality

    The Big Five and their whopping 33,000 doctoral A.I. researchers clearly indicate their intentions – to generate more corporate wealth.  According to a March 27, 2023 article written by the Washington Post, nearly 70% of A.I. Ph.Ds. opt to work for the corporate sector whereas, 20 years ago, that number was roughly 20%. This metric indicates that the vast majority of A.I. tools and technology being developed are not for academia or truly life-improving purposes, but for corporations to render them more machine-like and more easily generate and manipulate money.

    OpenAI CEO Sam Altman wrote a manifesto in 2021 predicting that the widespread deployment of A.I. would lead to most people being worse off than they are today. Altman painted an ominous picture of the world to come, decrying how “in the next five years, computer programs that can think will read legal documents and give medical advice. In the next decade, they will do assembly-line work and maybe even become companions. And in the decades after that, they will do practically everything, including making new scientific discoveries that will expand our concept of everything.” 

    Altman also argued that A.I. will “create phenomenal wealth,” and “if we get this right…can improve the standard of living for people more than we ever have before.” OpenAI conducted their own research into this topic in 2023 and published a paper indicating that approximately 80% of the U.S. workforce could have least 10% of their tasks affected by the introduction of GPTs (generative pre-trained transformers), while roughly 19% of the workforce could have as much as 50% of their tasks automated. The extent of unregulated image, text, and even voice manipulation by GPTs has the potential to create many copyright issues, especially for professional artists, musicians, and actors. 

    Copyright Infringement

    Public Citizen reported that artists and writers have had the content they produced and published online used without their consent to train A.I. tools to produce derivative art. Cartoonist Sarah Anderson’s artwork was turned into neo-Nazi memes by far-right political activists. Voice actors have similarly been impacted by non-consensual use of their voices with the use of A.I. tech. 

    Vice News reported on Feb. 7, 2023, that voice actors were increasingly subjected to contracts containing language that gives away their rights to use of their A.I.-generated voices.  (Demonstrating the high-wire act that online media is, Vice itself is reportedly headed to bankruptcy.)

    Tim Friedlander, President and founder of the National Association of Voice Actors said clauses “are very prevalent right now” that sign rights to an actor’s voice over to publishers. “[M]any voice actors may have signed a contract without realizing language like this had been added. We are also finding clauses in contracts for non-synthetic voice jobs that give away the rights to use an actor’s voice for synthetic voice training or creation without any additional compensation or approval. Some actors are being told they cannot be hired without agreeing to these clauses.” Actor Emma Watson’s voice was recently used without her consent for a reading of Mein Kamph, according to Vice News.  

    U.K.-based Getty Images has launched a lawsuit in federal court in Delaware against Stability A.I., alleging that the company copied 12 million images without permission to train its A.I. tools. Stability A.I. has responded to the complaint, arguing that their use of the images falls under the Fair Use Act 17 U.S.C. § 107 and does not constitute copyright infringement. Legal analysts believe that Getty Images has a stronger case than an individual artist would have given the blatant use of millions of its images. 

    Proposed Public Solutions

    Media attention surrounding A.I. tools and technology is accelerating. The Biden Administration acknowledged that policymaking was woefully lagging in mitigating potential harms stemming from the widespread deployment of A.I.  In response, the Biden Administration published a “Blueprint for an A.I. Bill of Rights” in October 2022. 

    This blueprint is intended to serve as a broad guide for the federal government’s deployment of A.I. and model of best practices for society at-large. 

    There are five principles outlined in the guidance document: 

    1) Americans should be protected from unsafe or ineffective systems.

    2) Americans should not face discrimination by algorithms. 

    3) Americans should be protected from abusive data practices and have agency over how data about them is used. 

    4) Americans should know when, how and why automated systems are being used to make decisions that affect them.

    5) Americans should have the choice to opt out of automated customer service and have access to a person who can help troubleshoot problems. 

    Critics of the blueprint argue that while the White House did seek input from the Big Five’s lobbyists, the guide “is essentially a white paper with no enforcement authority against Big Tech.” Some in the corporate world have already contested that, saying ,“even [the] unenforceable guidelines could stifle innovation.”

    U.S. Representative Ted Lieu (D-Calif.), who has a background in computer science, is advocating for the creation of a federal agency dedicated to regulating A.I. technologies. Lieu argues that Congress needs to implement the creation of this new agency to “ensure that the development and deployment of A.I. is done in a way that is safe, ethical, and respects the rights and privacy of all Americans, and that the benefits of A.I. are widely distributed and the risks are minimized.” 

    As the Big Five and other contributing A.I. companies continue their race to develop the newest and best A.I. technologies, people worldwide remain at risk for potential nonconsensual data collection, unwarranted marketing solicitation, and nonconsensual use of personal information, pictures, published text, and videos. This report highlights but a portion of the foreseeable legal issues arising in the unregulated Wild West of A.I. technology.

    [Editor’s Note: Would it be petty to point out that in the photo of Robots Typing some appear not to have heads? But, then, maybe their brains and eyeballs are located elsewhere. 😊 ]

    Tom Hagy edited and contributed to this article. 

    By Hunter Schmitz

    By Hunter SchmitzGuest Writer

    Hunter Schmitz is a freelance legal writer and paralegal with Focus on Property Law and Civil Litigation.

    How A.I. Can Benefit Society

    By ChatGPT

    Artificial intelligence has the potential to benefit society in a multitude of ways. One of the most significant areas of impact is in automation, where AI can perform repetitive and tedious tasks more efficiently and accurately than humans. This can lead to cost savings and increased productivity, freeing up people’s time to focus on more creative and strategic endeavors. Additionally, AI can help in areas such as healthcare by improving diagnostics and developing personalized treatment plans. It can also be used in education to provide personalized learning experiences and in environmental conservation to monitor and protect wildlife and natural resources. AI can also assist in disaster response and relief efforts by analyzing data and predicting outcomes. Overall, artificial intelligence has the potential to improve many aspects of society, from healthcare to education to the environment, and beyond.

    Can ChatGPT Really Pass the Bar?

    By ChatGPT

    As an AI language model, I do not have the ability to pass a bar exam or attend law school in the traditional sense. While I have been trained on a vast amount of legal information, including case law, statutes, and legal principles, I am not a licensed attorney and cannot provide legal advice or representation. However, I can assist in answering legal questions and providing information about legal topics. It is important to note that relying solely on information provided by an AI language model is not a substitute for seeking the advice of a licensed attorney.

    What is This Article About?

    By ChatGPT

    The article discusses the race among America’s Big Five tech companies – Amazon, Apple, Facebook, Google, and Microsoft – to develop artificial intelligence (AI) technology that they claim will change the world. The author raises concerns about the legal issues that may arise from an unregulated AI race, including degradation of free speech and public discourse, increased monopolization, greater economic inequality, and copyright infringement. The article also discusses how AI has already influenced the democratic process by being used to spread misinformation and generate fake news stories. The article further argues that the almost exclusive development of AI technology by the Big Five could lead to monopolization and limitations on free enterprise.

  • Pixel Litigation the Latest Craze in Privacy Law

    Pixel Litigation the Latest Craze in Privacy Law

    Meta, Google Face Barrage of Pixel Lawsuits in Digital Privacy War

    Photo by Amal S on Unsplash

    META PLATFORMS INC. AND GOOGLE  are currently facing nearly 70 lawsuits involving large companies and some hospital systems or individual health care providers utilizing Pixel tracking tools embedded on their websites and applications. Sensitive private data such as financial information gathered from filing tax returns online or patient healthcare information stored on patient portals is being actively tracked and sent to Meta and Google for both analytical and advertising purposes.

    Tracking pixels are a 1×1 Pixel graphic that serves as a snippet of code used for tracking user behavior, site conversions, web traffic, and other metrics generated from a site’s server. In 2018, Meta told Congress that there were more than 2 million Pixels across the web, which at the time, was one of the largest data-harvesting operations most internet users had ever seen. Meta makes their Pixel code freely available to anyone and any business – thus the amount of Pixel tracking has exponentially grown since Meta testified before Congress. The analytical information that companies gleam from Pixel tracking is paying off and is featured on everything from fast food companies such as Chick-Fil-A, media companies like iHeart Radio, and even tax-filing websites such as Tax Slayer or TaxAct.

    Pixel Tax Data

    On November 22, 2022, theverge.com co-published a report with The Markup, revealing that Pixel tracking tools located on several renown American tax-filing websites were sending individual tax filers’ contact and financial information to Meta and Google. From January to July 2022, The Markup tracked websites’ use of the Pixel as part of the Pixel Hunt in partnership with Mozilla Rally. Participants of the Pixel Hunt installed a browser extension that provided The Markup with a copy of all data shared with Meta through the Pixel. H&R Block, Tax Slayer, and Tax Act utilized Pixels on their websites and applications that sent financial data to Meta according to the data-driven report.

    TaxAct’s Pixel sent some of their users’ tax data to Facebook, including their filing status, adjusted gross income, and the amount of their tax return, if applicable. TaxAct says it has about “three million consumer and professional users”. The Pixel Hunt also revealed that TaxAct’s embedded Pixels were sending data to Google Analytics as well. The Pixel Hunt also revealed that Tax Slayer, H&R Block, and Intuit were also sending specific types of data to Meta and Google.

    The audit on Tax Slayer revealed that their embedded Pixel was gathering and sharing information such as phone numbers, the name of the user filling out the tax forms, and names of any dependent added to the return.

    An audit on Intuit, America’s largest online filing software, revealed that the company did employ a Pixel but did not send financial information to Meta, but instead sent usernames and information about the last time a device signed into the Intuit account. Whereas the audit into H&R Block revealed that information was being gathered and shared on filers’ health savings account usage as well as dependents’ college tuition grants and expenses.

    Tax filing is estimated to be an $11 billion industry in the United States with nearly 150 million individual returns filed electronically in 2021 according to this article. Free tax filing preparation and filing options do exist, but it’s limited to people making $73,000 or less and tends to be difficult to use.

    Utilizing the Pixel during their tracking, The Markup found that the Internal Revenue Service directs taxpayers attempting to file for free to some of these tax filing websites with embedded Pixels. TaxAct and Tax Slayer are part of an agreement known as the Free File Alliance. TurboTax (“Intuit”) and H&R Block had participated in this program in the past. Several days after this report was published, a class action lawsuit was filed against Meta in the Northern District of California, John Doe and Jane Doe v. Meta Platforms Inc., et al., 3:22-cv-07557.

    Pixel Healthcare and Patient Data

    Pixels are also utilized by some healthcare systems and individual medical providers in the United States. In another lawsuit regarding Pixel litigation against Meta in the Northern District of California, Jane Doe v. Meta Platforms Inc., et al., 3:22-cv-04293-AGT, the plaintiff alleges that at least 664 hospital systems or medical provider websites have sent data to Meta via its Pixel tracking tools. The plaintiff argues that this tracking of her private health information is in violation of the Health Insurance Portability and Accountability Act (“HIPAA”)

    HIPAA protects the privacy of individually identifiable health information by allowing only certain uses and disclosures of health data, such as for research purposes – but only if this data can’t be linked back to a particular patient. Currently under HIPAA, releasing data that is not properly de-identified could be considered a breach of HIPAA.

    Recently on January 30, 2023, a class-action lawsuit was filed in the Tenth Judicial District of Louisiana regarding a local health care provider, Willis-Knighton Medical Center using Pixel tracking tools to send sensitive patient health data to Meta. The plaintiff in Jacqueline Horton, individually and on behalf of others similarly situated v. Willis-Knighton Medical Center, 93767-B, brought action against Willis-Knighton Medical Center for ‘exposing highly sensitive personal information to third parties without their knowledge or consent.’ The Louisiana case differs from California’s because California is one of the handful of states that has passed a statute related to video privacy and consumer protection.

    In Jane Doe v. Meta Platforms Inc., the website allegedly shared information related to scheduling appointments with a doctor and reviewing test results. The California suit is seeking damages paid to consumers under the Video Privacy Protection Act (“VPPA”) 18 U.S.C. § 2710. This case was also brought under the California Confidentiality of Medical Information Act, that allows for damages of $1,000.00 per violation. In addition, the California court could potentially force hospital systems named in the suit to clearly disclose that their website uses Pixels to share data with Meta. The Plaintiff is also asking the judge to order that Meta delete sensitive health information that could be used to generate specific ads. This case will highlight misunderstandings of how HIPAA protects health information that’s in the hands of health care providers, insurers or any other entity currently subject to existing HIPAA provisions.

    Origins of Pixel Litigation Lawsuits

    The VPPA regulates the disclosure of information about consumers’ consumption of video content and imposes prescriptive requirements to obtain consumers’ consent to such disclosure(s). The law was originally enacted in 1988, a year after a journalist published Supreme Court Justice Robert H. Bork’s video rental history during his nominee process in 1987. The rental history contained no salacious details however and Congress quickly acted to pass the VPPA. The act reads:

    The VPPA prohibits a person or business that rents, sells, or delivers prerecorded “video cassette tapes or similar audio visual materials” from “knowingly disclos[ing], to any person, personally identifiable information concerning any consumer of such provider . . . .,” absent informed, written consent as defined by the VPPA. 18 U.S.C. § 2710(a)(3). If liability is found, the VPPA allows consumers to seek the following remedies – (1) statutory damages in the amount of $2,500 per violation, (2) punitive damages, and (3) recovery of attorneys’ fees. 18 U.S.C. § 2710(c).

    The VPPA was originally enacted to address the concept of a video tape service provider (“VTSP”). This was associated with traditional video rental stories and was rarely invoked as of lately. As online video services became more prevalent, the VPPA began to create legal barriers to major businesses and marketing opportunities for them. Prior to Congress amending the VPPA in 2013, the law created a strange legal paradigm: An organization’s business model involving the provisions to consumers, either on a standalone basis or as part of its broader online platform of online video content (such as a social media company), makes the organization qualify as a VTSP.

    Congress amended the VPPA in 2013 to provide that disclosure of consumer data to third parties is not wrongful if the consumer elects to give ‘informed, written consent in a form that is distinct and separate from any form setting forth other legal or financial obligations of the consumer at the time the disclosure is sought, or in advance for set period of up to two years.

    Under the amendment, the VPPA does provide a number exceptions that permit information being disclosed to third parties. Remarkably, one of those exceptions allows the sharing of information about the user ‘to any person if the disclosure is solely of the names and addresses of consumers and if: (i) the VTSP has provided the consumer with the opportunity, in a clear and conspicuous manner, to prohibit such disclosure; and (ii) the disclosure does not identify the title, description, or subject matter of any videos or other audio-visual material; however, the subject matter of such materials may be disclosed if the disclosure is for the exclusive use of marketing goods and services directly to the consumer.’

    These exceptions allow the VPPA to permit the disclosure of the name and address of the user together with the identify of the VTSP and subject matter of the video content so long as the intended purpose is for direct marketing. The VPPA has since been challenged in several distinguishable cases decided in 2015 primarily on the grounds of violation of privacy.

    Recent Developments in Pixel Litigation

    The VPPA has come under consumer and legal scrutiny in recent years. Several important legal rulings have largely curtailed individual and collective efforts to declare violations under the VPPA. In Ellis v. Cartoon Network Inc., 803 F.3d 1251 (11th Cir. 2015), it was opinioned that, Consumers who use free mobile applications do not quality as ‘subscribers’ under the VPPA. The Ninth Circuit Court also opinioned two cases in 2015 regarding exceptions to the VPPA.

    In Rodriguez v. Sony Computer Entm’t Am., LLC, 801 F.3d 1049 (9th Cir. 2015), an intra-corporate disclosure of personal information does not violate the VPPA. Then it was also decided by the 9th Circuit Court in another 2015 opinion Mollett v. Netflix Inc. 795 F.3d 1062 (9th Cir. 2015) that VTSPs cannot be held liable under the VPPA for circumstances where subscribers’ personal information was displayed on devices, such as televisions, that could potentially be viewed by third parties. This Court said that ‘viewing of such devices was beyond the companies’ control.’

    These recent rulings narrowed the scope of the VPPA and helped provide definitions for the outdated video-store era law. Civil lawsuits across the nation related to Pixel litigation continues to barrage the integrity of the VPPA.

    IHEARTMEDIA, Inc. is facing a lawsuit for allegations of violations of the VPPA in the Middle District of Florida Gloria Talley, individually and on behalf of herself and all others similarly situated v. IHEARTMEDIA, Inc., 8:32-cv-00215. Similarly the popular chicken chain, Chick-Fil-A is facing a similar class action lawsuit in the Northern District of California in Keith Carroll, individually and on behalf of all others similarly situated v. Chick-Fil-A, Inc., 3:23-cv-00314.

    As lawsuits continue to mount against Meta and Google, the integrity of the VPPA is thrown into question. It is likely that one of the pending actions across the nation will eventually land the law itself into further judicial review, or if Congress acts, could create an entirely new blanket law altogether to help address the rapid interference and sharing of consumer data.

    By Hunter Schmitz

    By Hunter SchmitzGuest Writer

    Hunter Schmitz is a freelance writer and paralegal with Focus on Property Law and Civil Litigation.

  • EMR Audit Trail—What Is It? Why Do They Matter? What Should You Look For? by Haley K. Grieco and Brooke E. Reddin

    EMR Audit Trail—What Is It? Why Do They Matter? What Should You Look For? by Haley K. Grieco and Brooke E. Reddin

    The Authors

    Haley Grieco

    Haley GriecoHall Booth Smith

    Haley K. Grieco (hgrieco@hallboothsmith.com) is a partner in the Paramus, New Jersey, office of Hall Booth Smith, where she defends physicians, hospitals, and other healthcare providers in a wide range of medical malpractice litigation.

    Brooke Reddin

    Brooke ReddinHall Booth Smith

    Brooke E. Reddin (breddin@hallboothsmith.com) is an associate with the firm, where she focuses her practice on healthcare, medical malpractice, and aging services litigation.

    The Journal on Emerging Issues in Litigation

    Emerging Litigation Podcast

    Emerging Litigation PodcastProduced by HB Litigation and Law Street Media

    Interviews with leading attorneys and other subject matter experts on new twists in the law and how the law is responding to new twists in the world.

    EMR Audit Trail—What Is It? Why Do They Matter? What Should You Look For?

    “As the healthcare industry becomes increasingly digitized, it is imperative that attorneys appreciate the impact it may have on their clients and their practice. In medical malpractice matters, discovery requests for metadata—specifically, the production of the EMR audit trail—has steadily increased over the past few years.”

    Abstract: Maintaining electronic medical records, or EMRs, is now a nearly universal best practice among medical providers from small physician practices to large hospital networks. Unlike handwritten or typed records, these digital documents carry with them much more data than meets the eye. In this article, the authors—two medical malpractice attorneys— discuss what attorneys need to know about EMRs in the litigation context and the metadata bread crumb trail they leave behind. They discuss the types of data involved, federal requirements, discovery considerations, privacy implications, and the pros and cons and risks of using these records in defending healthcare providers.

    During the past ten years electronic medical records (EMR) have all but rendered obsolete handwritten medical records. Medical providers have had to learn  computer systems, programs, software, hardware, and forms like never before. When hospitals, facilities, and medical offices change EMR systems, the process of learning the new system starts over. But what about the data you do not see? What lurks beneath the surface of the records that providers never see?

    This article looks at EMR from the perspective of the individual seeking to understand the data retrospectively in the context of a pending litigation rather than the requirements for those developing and maintaining EMR.

    Download the article now!

  • Cybersecurity and Data Privacy Year in Review 2021

    Cybersecurity and Data Privacy Year in Review 2021

    The Authors

    The authors are all attorneys with the Kennedys law firm (kennedyslaw.com). Joshua Mooney (joshua.mooney@kennedyslaw) and Judy Selby (judy.selby@kennedyslaw.com) are partners. Tracey Kline (tracey.kline@kennedyslaw.com) and Alexis Childs (alexis.childs@kennedyslaw.com) are associates. Bridget Mead, associate, and Javier Vijil, senior associate, also contributed to this article.

    Judy Selby is also a member of the Editorial Board of Advisors for the Journal on Emerging Issues in Litigation.

    The Journal on Emerging Issues in Litigation

    Cybersecurity and Data Privacy 2021 in Review

    By Joshua Mooney, Judy Selby, Tracey Kline, and Alexis Childs

    Abstract:

    As the world emerged from lockdown, it should come as no surprise that cybersecurity and data privacy remained dominant topics in the media and legal industry. Some of 2021 was much like 2020—ransomware attacks continued to fill the headlines, and in the aggregate, constituted significant loss paid under cyber insurance policies. OFAC reminded victim companies and incident response firms (and cyber carriers) that it remains unlawful to pay ransom payments to designated organizations. Comprehensive federal legislation addressing cyber defenses and notification requirements never materialized. Yet in 2021, we saw new and significant developments. U.S. law continued its drift toward comprehensive privacy regulation with two new significant pieces of privacy legislation and California’s enforcement of the California Consumer Privacy Act. In the absence of federal legislation, federal agencies either stepped up enforcement actions or signaled that they intend to do so within their realms of governance. Litigation under the Illinois Biometric Information Privacy Act continued its surge while the Illinois high courts rendered two impactful decisions and a circuit court punted to Illinois’s highest court. This review provides a brief synopsis of many events and developments that made the authors’ list.  

    Perhaps one of the most significant developments in U.S. privacy law for 2021 was the enactment of comprehensive data privacy laws in Virginia and Colorado. Both pieces of legislation, which go into effect in 2023, adopt frameworks resembling those in the EU General Data Protection Regulation 2016/679 (GDPR) and the California Consumer Privacy Act (CCPA). Both laws also grant consumers significant rights with respect to their personal data, but neither contains a private right of action. 

    Get the article now!

  • Broken Privilege and IoT with Kathryn Rattigan

    Broken Privilege and IoT with Kathryn Rattigan

    Broken Privilege and IoT with Kathryn Rattigan

    Broken Privilege IOT Kathryn Rattigan

    Joining me to discuss this emerging area of law is Kathryn M. Rattigan, a member of the Business Litigation Group, the Data Privacy + Cybersecurity Team, and the Drone Compliance Team in the Rhode Island office of Robinson Cole.

    Kathryn provides clients guidance regarding privacy and data protection in connection with mobile devices, data storage technologies, mobile apps, and location-based services. She  assists with the development of website and mobile app privacy policies and  terms and conditions. Kathryn is a frequent contributor to the excellent Robinson Cole Data Privacy + Cybersecurity Insider blog.  She holds a J.D. from the Roger Williams University School of Law and a B.A. (magna cum laude) from Stonehill College.

    This podcast is the audio companion to the Journal on Emerging Issues in Litigation, a collaborative project between HB Litigation Conferences and the Fastcase legal research family, which includes Full Court Press, Law Street Media, Docket Alarm and, most recently, Judicata. If you have comments or wish to participate in one our projects, or want to tell me how insightful and informative Kathryn is, please drop me a note at Editor@LitigationConferences.com.

    Finally, yes, “skeevy” is a word. And the law is not settled as to whether Shiloh has privacy rights.

    Tom Hagy
    Host of the Emerging Litigation Podcast

    There are now billions and billions of interconnected devices in the world with more coming online every day. Smart cars. Smart cities. Smart agriculture and so much more. Even our pets are connected.

    And you have to look no further than the Colonial Pipeline ransomware attack to see the real-world consequences of what criminals can pull off by connecting with things large and small.

    Worried about your privacy? Well. There is plenty to worry about.

    Fortunately we also have a lot of people fighting back on the technical, security, law enforcement, and legal fronts.

  • The Commercial Drone Industry: Privacy, Security, Threats, and Mitigation of Risk

    The Commercial Drone Industry: Privacy, Security, Threats, and Mitigation of Risk

    HB presents a CLE-eligible webinar
    Now on-demand at the West LegalEdcenter
    THE COMMERCIAL DRONE INDUSTRY
    Privacy, Security, Threats, and Mitigation of Risk

    Drones have become an increasingly valuable tool for businesses of all types and sizes.

    Drones are already being used in many applications, but more will certainly arise as the technology advances. This means that certain risks, like cyber threats, will also continue to present themselves. Protecting the transmission and storage of data collected through drones is critical.

    Unfortunately, security usually comes as an afterthought. The drone industry is part of the aviation industry, which, based on its knowledge, keeps safety as a number one concern. Part of that safety is having proper protection for your systems, including security as a fundamental design principle.

    Take this webinar to gain insights on the topics listed below, and shared by an attorney who practices on the cutting-edge of this evolving technology.

    Topics:

    • Defining drones.
    • Current and future applications.
    • FAA Modernization and Reform Act of 2012.
    • FAA Part 107 Regulations and waivers.
    • Resources, e.g. the FAA Drone Zone and LAANC Portal.
    • Penalties for violations.
    • Privacy implications.
    • Drones as weapons.
    • Vulnerability to cyber attacks.

    Take it now!

    What you get:

    1+ CLE credits (subject to bar rules).

    Insights from an experienced professional who specializes in this area of the law.

    The complete PowerPoint presentation.

    Continued access to the complete recording for later use.

    Answers to your questions.

    Fee:

    No additional charge to subscribers to the West LegalEdcenter.

    Non-subscribers may take the course for $170.

    Meet the Speaker

    Kathryn Rattigan
    Robinson & Cole LLP

    Kathryn Rattigan is a member of the firm’s Business Litigation Group and Data Privacy + Cybersecurity Team. She advises clients on data privacy and security, cybersecurity, and compliance with related state and federal laws. She assists clients in assessing risks related to technology and software contracts, as well as with compliance-related issues with outsourcing and vendor management. She represents clients across all industries, such as manufacturing, insurance, health care, education, energy, and construction.

    Kathryn helps clients comply with all state and federal regulations related to data privacy and cybersecurity. She is also a member of the firm’s Drone Compliance Team. As such, she advises clients on all legal issues surrounding the use of commercial drones, including navigation of Federal Aviation Administration regulations, commercial registration requirements, and Part 107 waivers.

    She is committed to doing pro bono work and being involved in the community. Her recent efforts include assisting Inner Explorer, a non-profit which works to help students focus and succeed through mindfulness practice in the classroom, and College Visions, which helps low-income students pursue a college education.

    She writes for two of the firm’s blogs, Data Privacy + Security Insider and Health Law Diagnosis.

    More about Kathryn

    Also, listen to my interview with Kathryn for the the Emerging Litigation Podcast!

    –Tom Hagy