Tag: Data Breach
-
Cyber Risks Enter a New and Increasingly Vicious Phase
For anyone plotting the evolution of cyber risks, the last phase of cyber-attacks was dominated by breaches that resulted in lost or stolen personal or financial data that could then be monetized.
The current phase is different.
“We have observed a significant increase in the number of disruptive breaches that our clients are dealing with,” says Charles Carmakal, Vice President at Mandiant/FireEye. “These involve destruction, extortion, or public shaming.”
How are organizations dealing with this shift?

“It’s catching many organizations off guard. Most don’t have a playbook for dealing with extortion,” Carmakal says. “While they may have thought about a ransomware situation, that’s different from the more common type of extortion we are seeing these days, where a threat actor threatens C-level executives or corporate board members with the release of sensitive information.”
“Many organizations assume the default is they wouldn’t give into the demands, but when in the middle of a crisis too often the decision is made to pay the threat actors,” he says.
“So it’s important to consider what your organization will do in this situation. For example, who will be involved in the decision-making process? Organizations should play out an extortion scenario so they have a plan when faced with real demands.”
How can organizations better test the efficacy of their security capabilities?
Many organizations conduct penetration testing or red-teaming exercises, but they often undermine their own efforts.
“A problem arises when an organization contracts a third-party to test their capabilities, but puts a lot of restrictions on those who are doing the testing,” Carmakal says. “For example, they will tell the testing team or red team to identify vulnerabilities, but not to exploit them, or they can exploit a vulnerability but stop there and not dig any further. The penetration testers might be allowed to test only during a certain day of the week or certain time of day. Or they might be allowed to sample only a fraction of the organization’s IP addresses and ignore everything else.”
“What happens is the penetration testers are not permitted access to the crown jewels,” Carmakal warns. “They can’t demonstrate business impact to the organization. This creates a false sense of security because the organization can say they had a team of qualified people try and fail to break into the network, but in reality they were unable to break through because of all the unrealistic restrictions imposed on that team.”
This false sense of security travels to the top. “Testing results are shared with the board and the board believes that because a really good third-party was not able to get to the crown jewels that they have a much safer environment than they really do. That’s a very common theme we see across the industry,” Carmakal says.
How do penetration testers deal with unrealistic testing parameters?
 “It’s part of the education process,” he says. “When a company wants us to do a very limited test, and we believe our reports will be shared with the leadership team or the board, then we just won’t take the engagement. We try to make it clear that this is not an exercise to make anyone look bad, but a way to leverage the lessons from all the bad guys who are breaking into organizations so you can strengthen your security.”
In the end, he says, “It’s better we identify the vulnerabilities than have the bad guys do it.”
What the geopolitical trends you are seeing?
Iran – “They used to be unorganized. They even clumsily posted social media profiles of themselves,” Carmakal says. “But they have become much more organized, more structured, more technologically adept, and have affiliated with government entities.”
“In 2017 we saw more intrusions from Iran than we had ever seen before. There was a noticeable spike in offensive intrusions coming from them. For some reason, in 2018 we really haven’t seen Iran targeting organizations in the United States. They’ve scaled back significantly in the US, but are still active in other parts of the world.”
“What makes security professionals nervous about Iran,” Carmakal says, “is that they are a wildcard. You don’t know what they are going to do. You don’t understand the rationale behind their activity. But what we do see is a capability and a willingness to be incredibly destructive – taking down businesses and publicly shaming organizations. The fact that they’ve slowed down their attacks on U.S. organizations is interesting, but we expect that to change.”
Russia – “Russia is not hacking the U.S. midterm elections like they were with the presidential election in 2016, but they are conducting some significant offensive operations around the world. They are very capable. They are also very good at disinformation and throwing false flags, so when you investigate them it’s difficult to tell who they really are. Russia is one of the few countries that demonstrates the willingness and capabilities to cause kinetic consequences through cyber-attacks, such as when they turned off the lights in Ukraine.”
In March 2018 The New York Times wrote, “The Trump administration accused Russia … of engineering a series of cyber-attacks that targeted American and European nuclear power plants and water and electric systems, and could have sabotaged or shut power plants off at will.”
When asked about this and the reporting that surrounded it, Carmakal said the story was a bit “sensationalized” and not 100% accurate. “While the intrusion was serious, we didn’t see the Russian actors getting anywhere near being able to shut off the lights,” he said, adding that they “certainly have the capability” in other parts of the world.
China – There has been a “notable decrease” in cyber intrusions from China since the 2015 bi-lateral cyber agreement was reached between President Obama and China’s President Xi, Carmakal says. While narrow in scope, addressing economic espionage — China’s state-sponsored theft of private U.S. intellectual property and then turning it over to state-owned and private companies in China — the agreement does appear have helped, reports suggest. “They are still hacking organizations and are following a defined playbook. We’re keeping a close eye on them to see how their offensive operations evolve,” Carmakal says.
North Korea – Except for the highly publicized attack against a major U.S.-based entertainment company, “North Korea rarely goes after Western organizations.” Given the country’s need for cash, “their focus has been more on robbing digital currency exchanges and stealing from banks digitally,” Carmakal says, adding that they, like Iran, are a bit of a “wild card.” North Korea actors have stolen more than $100 million from victims, Carmakal says.
You will be able to hear insights like these, and updates on anything that occurs between now and December in Bermuda when Carmakal and his fellow panelists discuss important trends in global cyber risks.
This posted was edited by HB Founder & Managing Director Tom Hagy. In the 1990s Tom launched one of the first nationwide legal reports in this area — Mealey’s Litigation Report: Cyber Tech & E-Commerce — when he was publisher at Mealey’s, now part of LexisNexis. If you are interested in posting on this site or discussing speaking opportunities, please contact us at Editor@LitigationConferences.com.
-
Protecting Intangible Assets: Risk Transfer Market Yet to Catch Up
Intrinsically Intangible.
by Giles Harlow, Senior Vice President, Aon (Bermuda) Ltd.
 In the early 1980’s, tangible assets made up around 80% of the value of the S&P 500. Fast forward to today and nearly 85% of the value of the S&P 500 is attributable to intangible assets.
However, the risk transfer market has not caught up. According to the Aon/Ponemon report of last year, whilst around 60% of tangible assets (property, plant and equipment) are currently being insured, only 12% of informational assets are.
So what gives?
If the vast majority of companies’ values in 2018 are attributable to intangibles, why are they not transferring those risks? Is it a lack of education on the client side? A lack of innovation in the brokerage community? A lack of understanding or willingness to accept these new risks on the carrier end? Or is it that whilst the marine and property markets have had centuries to evolve, the newer intangible insurance markets are just gearing up to size as they collate the data they need to properly price and model these risks?
Likely, it is some combination of all of these factors. We have seen great strides in the cyber market, with double-digit premium growth over the last four-to-five years. The market has evolved from being focused on large data holders, to providing products which contemplate the cyber perils affecting manufacturers, the transportation industry and other non-data holders. “Business interruption” has quickly morphed into “system failure coverage.” “Contingent business interruption” now looks more akin to full supply chain risk, not just for IT service providers but now contemplating all vendors. “Bodily injury” and “property damage” stemming from non-physical threats complete the circle back into tangible loss being covered under cyber policies.
Intellectual property — hands down — makes up the largest dollar percentage of the intangible asset value of the S&P 500. This has long been a conundrum for the industry as a whole – both in terms of how to value the asset and, more so, how to value the loss. Again, we have seen great momentum here with much larger limits than were historically available now obtainable from the markets both as a theft product as well as being offered for IP infringement. Even now carriers are contemplating supporting the multi-trillion dollar asset class of intellectual property when used as collateral. This could dramatically impact both the equity financing model and asset backed lending world we know today.
Clearly the will to innovate is alive and well within the industry. It is tough to price emerging risk when the models that our industry are built on rely on historical data, data that is often out of date or irrelevant in these rapidly evolving intangible classes of business. New ways to price and structure these insurance purchases have to be found in order to maintain the industry’s relevance in today’s world.
Bermuda is at the forefront of many of these initiatives and its underwriters and brokers are constantly seeking to raise the bar to address evolving client need. The panel titled “Evolution of Product and Buyer” will be tackling these and more topics in detail at the Dec. 6-7, 2018, International Cyber Risk Management Conference, or ICRMC, in Bermuda from the perspective of brokers, underwriters and insurance purchasers.
Get 10% off the registration fee with promotion code HB2018.
http://www.aon.com/risk-services/cyber.jsp
http://www.aon.com/risk-services/amats/intellectual-property-solutions.jsp
-
Financial Services Cyber Risk Information Sharing
Why We Need to be More Like Apes, Less Like Seagulls
By Tom Hagy
Featuring Craigg Ballance, Director of Canadian Member Services, FS-ISAC
Even before we can walk we are encouraged to share. We’re told to share our things even when we barely have any. Even some wild animals share food and resources – even when those resources are scarce. Some creatures are better at it than others, of course. Apes and lions? Absolutely. Seagulls? All you have to do next time you’re on the beach is toss what’s left of your ham sandwich into the air and see how generous gulls are.
People fall into sharing — and not-fond-of-sharing — groups, too. Sharing is particularly critical in the financial sector where, while privacy and security regulations command a tight lid on data, global financial institutions are successfully sharing data about cyber risk, says Craigg Ballance, Director of Canadian Member Services for FS-ISAC in Toronto. But, he says, sharing has to take place across a broad landscape.
“Information analysis sharing has to cut across the various subsets of the financial sector,” says Ballance. “While banks share local data, they are trying more and more to share globally, but,” he says, “banks need to share with other institutions, like insurers, investment funds, pension funds, and other types of financial institutions, for this cooperation to have the greatest and most effective impact on security.”
While some IT professionals may tend to want to play things close to the vest, when it comes to cybersecurity teams it is the IT professional who works openly with others who is an invaluable player.
The Danger of Over-Confidence
Some blamed over-confident IT professionals for the massive cyber attack that temporarily crippled shipping giant Maersk in June 2017. At the same time, as reported by Reuters on June 27, 2017, Ukrainian commercial banks also sustained a cyber attacks.
“There are a lot of smart people out there actively trying to figure out ways to mess us up,” Ballance says, whether it’s through new denial of service attacks, or cyberware and ransomware, or the creatively diabolical phishing attacks. “When one entity is falls prey to one of these schemes we’re suddenly all at greater risk,” Ballance says. “There is a limited volume of resources and talent to combat cyber-attacks, so pooling resources, information and skill sets is critical.”
Ballance emphasizes the importance of having a playbook so when a crisis occurs people know who is supposed to do what and when. “In the midst of an attack people tend to lose their minds and not necessarily act logically,” he says. “So having a prepared methodology to get your organization out of a pickle is a piece of work we strongly advocate, as well as sharing that methodology across industries. This way, as examples, banks and insurance companies and investors can enrich each other with new insights and skills.”
He also advocates simulated attacks and table-top exercises so people can engage as if they are dealing with a real disaster, like those conducted by FS-ISAC. Conducting post-event analysis to improve response and sharing those findings is also important.
Experience tells us that when it comes to global cybersecurity we need to be more like gorillas and big cats than selfish seagulls down by the sea shore.
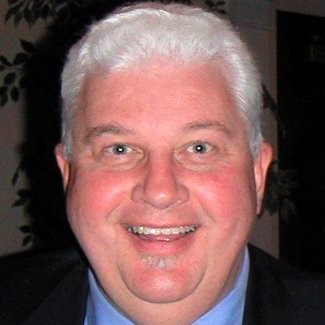 Craigg Ballance will share insights like these and more at the International Cyber Risk Management Conference Dec. 6-7, 2018 in Bermuda. He will be joined by Nick Galletto, Global Cyber Risk Services Leader at Deloitte in a session titled, “Strength Through Information Sharing Within the Global Financial Services Arena.”
Over the past three-plus decades, Ballance has led and managed advanced technology-enabled business initiatives across a wide range of competitive sectors, countries and areas of innovation. These build on his experience in leading electronic commerce development in one of the world’s path-setting banks in the field and on his extensive work in finance, logistics, international business and government. He is the author/co-author of three books on leveraging technology for business innovation.
Tom Hagy is a Philadelphia-based writer and entrepreneur, Founder and Managing Director of HB Litigation Conferences LLC and Custom Legal Content LLC, former Editor and Publisher of Mealey’s Litigation Reports, and a former Vice President at LexisNexis®.
-
Francoise Gilbert on Colorado’s New Privacy Law: Are You Ready?
Effective Sept. 1, 2018, Colorado will require all entities that process or store certain personal information of Colorado residents, regardless of whether the entity is located within or outside of Colorado, to have formal data security and data disposal programs. This is the result of the adoption of Bill 18-1128 “Concerning Strengthening Provisions for Consumer Data Privacy,” signed into law at the end of May 2018, to amend and supplement existing law …. Previously, the definition of “personal identifying information” under the Colorado law was limited to a resident’s first name or initial and last name in combination with the individual’s Social Security, driver’s license, or identification card number, or a credit or debit card or bank account number, combined with a password or access code. The new definition includes additional forms of identification, such as student, military, passport, and health insurance identification number, as well as other types of information, such as medical information or biometric data. It also includes username or e-email address in combination with a password or security question answers that would permit access to an online account …. Organizations that collect personal identifying information of Colorado residents and that do not yet have the written programs necessary to formalize their data protection practices urgently need to focus on compliance. — Francoise Gilbert, Greenberg Traurig
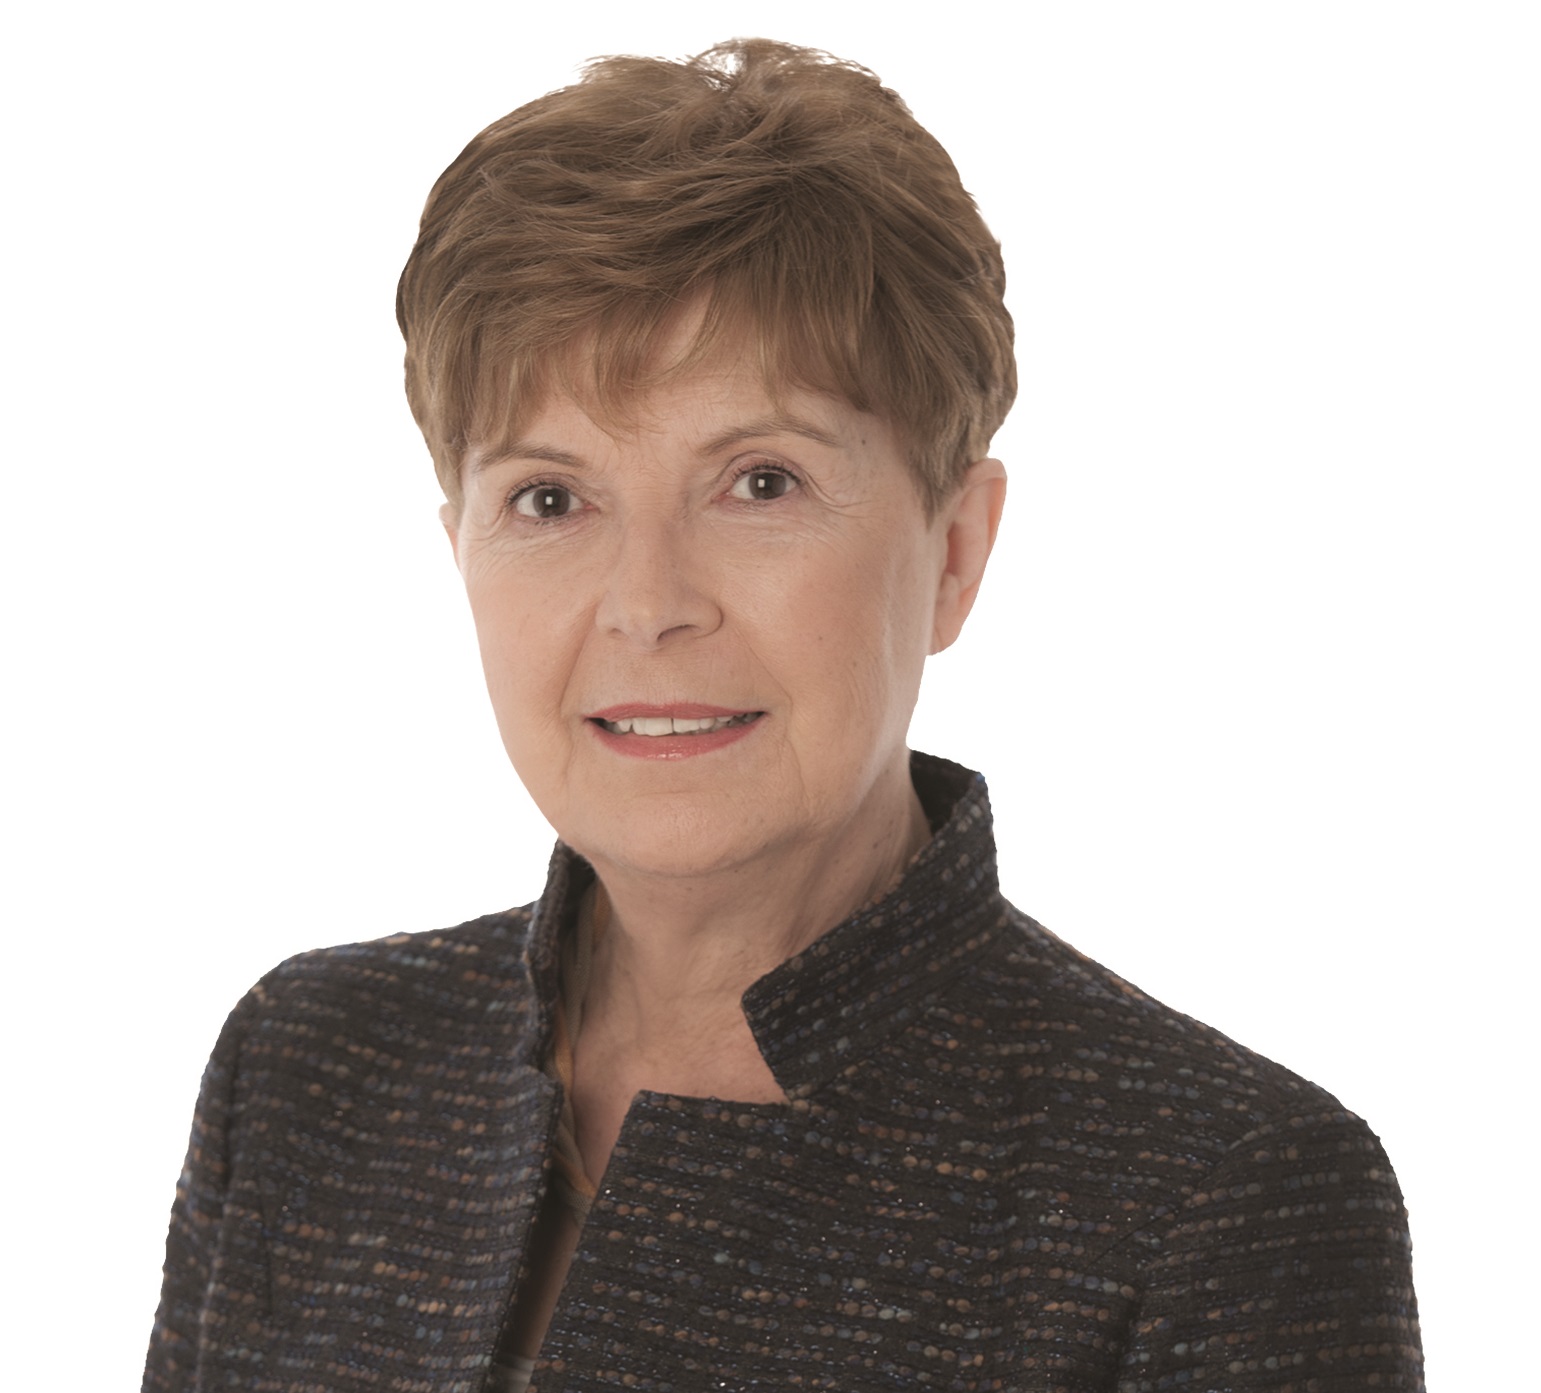 Francoise Gilbert, a partner at Greenberg Traurig, is the author of the two volume treatise “Global Privacy and Security Law” (Wolters Kluwer Publishing), covering 68 countries. Her practice has focused on information privacy and security for more than 25 years. She advises clients on the entire spectrum of domestic and international privacy and cyber security issues legal issues, such as Internet of Things, smart cities, artificial intelligence, analytics, digital advertising and other cutting-edge developments that rely on the extensive use of personal data.
She is one of the featured speakers at the Privacy+Security Forum which takes place Oct. 3-5, 2018, in Washington, DC.
-
A.I. Best Practices: Rules and Policies for Using Artificial Intelligence in Your Business
Explore how cybersecurity breaches impact insurance, risk management, and data privacy with evolving legal and compliance challenges.
[one-third-first]
DATE: Sept. 27, 2018
TIME: 2 p.m. EDT; 1 p.m. CDT; 12 p.m. MDT; 11 a.m. PDT
PLACE: Your computer or mobile device
PRICE: $197* per dial-in site
*Price is good through Aug. 16. After that it’s $247.GROUPS ARE GOOD: Registering qualifies you to multiple attendees at your location.
CLE: 1 credit
Please send CLE questions to
CLE@LitigationConferences.comSPEAKER:
John Frank Weaver
Attorney
McLane Middleton

Your registration includes:
• A site license to attend this webinar (invite as many people in one location as you can fit around your computer at no extra charge).
• Downloadable PowerPoint presentations from our speakers.
• The opportunity to connect directly with speakers during the audience Q&A session.
• At least one-hour of CLE credit.
Produced in collaboration with
and their new
Journal of Robotics, Artificial
Intelligence & Law
[/one-third-first] [two-thirds]
Nearly every industry is adopting or preparing to adopt artificial intelligence applications into their business practices.
That’s exciting. However, there are almost no government regulations for their use and few resources providing best practices that anticipate ethical considerations and forthcoming legal requirements.
This lack of direction poses a serious problem as A.I. applications become more widespread. Businesses are creating their own ad hoc practices without considering the eventual government oversight and ethical consensus, which will result in costs and potential liability later when those companies have to change their practices.
This webinar looks at how your company should approach its A.I. rules and policies in order to minimize the impact of expected government action and cultural norms.
Register now and join our speaker as he explores existing laws addressing privacy and data security, pending A.I. legislation at the state and federal levels, and the recommendations of federal agencies that are most likely to be codified.
The webinar will provide practical guidance for attendees to use when developing internal rules, policies, practices, contracts, and public facing documents. The speaker will rely on relevant existing laws, proposed legislation, and reports from federal agencies that advocate certain public policies for the governance of AI.
What you will learn:
1. The requirements of privacy laws – including GDPR, Canada’s PIPEDA, and the new California privacy statute – that have special application to A.I.
2. Best practices for drafting a public facing privacy policy that addresses your use of A.I.
3. Best practices for preparing internal rules and policies governing your employees’ use of A.I.
4. Best practices for bots and other forms of A.I. that interact with consumers.
5. Best practices for A.I.-specific terms of use and consents.
6. Best practices for addressing A.I. in employee contracts and handbooks.
7. Best practices for addressing A.I. in vendor contracts, including assignment of liability and indemnification obligations.
And more!
Attendees will be able to go back to their companies and review their current A.I. practices, policies, and rules to determine how appropriate they are in light of expected regulations and expectations. The ultimate goal is to avoid costly revisions in response to evolving consumer expectations and government requirements. A little investment now could potentially save a lot of money in revisions changes, PR, and remediation later. — John Weaver, speaker
Speaker
 The webinar speaker, John Frank Weaver, is an attorney with McClane Middleton whose practice focuses on A.I. and autonomous technology. He is the author of Robots Are People Too: How Siri, Google Car, and Artificial Intelligence Will Force Us to Change Our Laws, a contributing writer at Slate focusing on legal issues implicated by AI and autonomous devices, and a columnist for and member of the board of editors of The Journal of Robotics, Artificial Intelligence & Law.
[/two-thirds]
-
Joshua Gold on Cyber Crime and Insurance
With the amount of trickery going into thefts and embezzlements these days, crime insurance companies too often use the many steps involved in a fraudulent scheme to argue that losses are indirect and otherwise uncovered.
The recent decisions of the Second Circuit and Sixth Circuit on the “direct loss” argument and the scope of computer fraud coverage are important victories for policyholders generally, making clear that where the predominant step in the chain is some type of covered fraudulent misconduct involving a computer, a court is not going to entertain a direct loss defense to excuse the insurance company from paying.
As such, policyholders should be familiar with their crime coverage and promptly notify all potentially implicated lines of insurance coverage when a cybercriminal is afoot. — Joshua Gold, Anderson Kill
Read Josh’s complete article.
Joshua Gold is Chair of Anderson Kill’s Cyber Insurance Recovery Practice and was amicus counsel for United Policyholders in the Medidata Solutions, Inc. v. Federal Insurance Company case before the Second Circuit.
-
Willis Towers Watson: Cyber Risk Top D&O Concern
Based on their survey, Willis Towers Watson says cyber risk continues to top the list of concerns for directors and officers (right up there with employee claims). As for coverage, while they care about price, things like their relationship with the carriers and how well they handle claims are critical elements.
And, maybe one key reason cyber events keep happening: “Only 13% of board members feel that their organizations learn from past cyber mistakes.”
Read the results of the Willis Towers Watson survey.
-
BitSight Releases eBook on Use of A.I. & Big Data in Continuous Cyber Risk Monitoring
“With every reported data breach or cyberattack, the cyber risk landscape gets a little more complex. Cyber criminals create new attack vectors, cybersecurity professionals develop new controls to protect their systems, the criminals get to work circumventing the controls, and so on.The result of this back and forth is that cyber risk professionals have a huge variety of risk factors to worry about. In response, risk managers and security specialists need to develop extremely complex cybersecurity programs to make sure all of their bases are covered.
“With so many cybersecurity risks to consider, it’s inevitable that some will receive less attention than they deserve. Unfortunately, these overlooked risk factors could play a role in your next cyberattack, and if your financial services firm isn’t prepared, that could be extremely costly.” Read more.
We’re looking forward to seeing the BitSight team in Bermuda Dec. 6-7, 2018, at the International Cyber Risk Management Conference.
-
Crowell & Moring on D&O Corporate Liability for Cyber Claims
“Although many commentators have noted the potential exposure for cyber claims in the form of shareholder actions under D&O coverage, little attention has been given to the risks of cyber exposure under Side C [D&O corporate liability] coverage,” write Laura A. Foggan and Thomas Kinney of Crowell & Moring LLP. “D&O policies contain many exclusions and coverage limitations that should protect against undue, unintended expansion of such policies to encompass cyber risks. However, as this case illustrates, courts may not always agree that those coverage limitations fully address cyber breach exposures.”